

Strengthen Threat Intelligence with SoldierX AI SIEM
Modern cyberattacks follow structured tactics, techniques, and procedures (TTPs) that can be difficult to interpret without a standardized framework. SoldierX AI SIEM’s MITRE ATT&CK Mapping feature helps security teams map incidents directly to the MITRE ATT&CK framework, providing deep visibility into attacker behavior. By translating raw security events into known attack techniques, SoldierX AI SIEM enables faster investigations, smarter prioritization, and alignment with global cybersecurity standards.
Core Advantages
Key Benefits
Technique-Based Mapping
Map incidents to specific MITRE ATT&CK techniques such as credential access or lateral movement.
Prioritized Response
Focus on high-risk techniques based on their severity and real-world prevalence.
Standardized Analysis
Align incident response with the globally recognized MITRE ATT&CK framework.
Threat Hunting
Identify and investigate IOCs based on mapped ATT&CK techniques.
Process Overview
How It Works
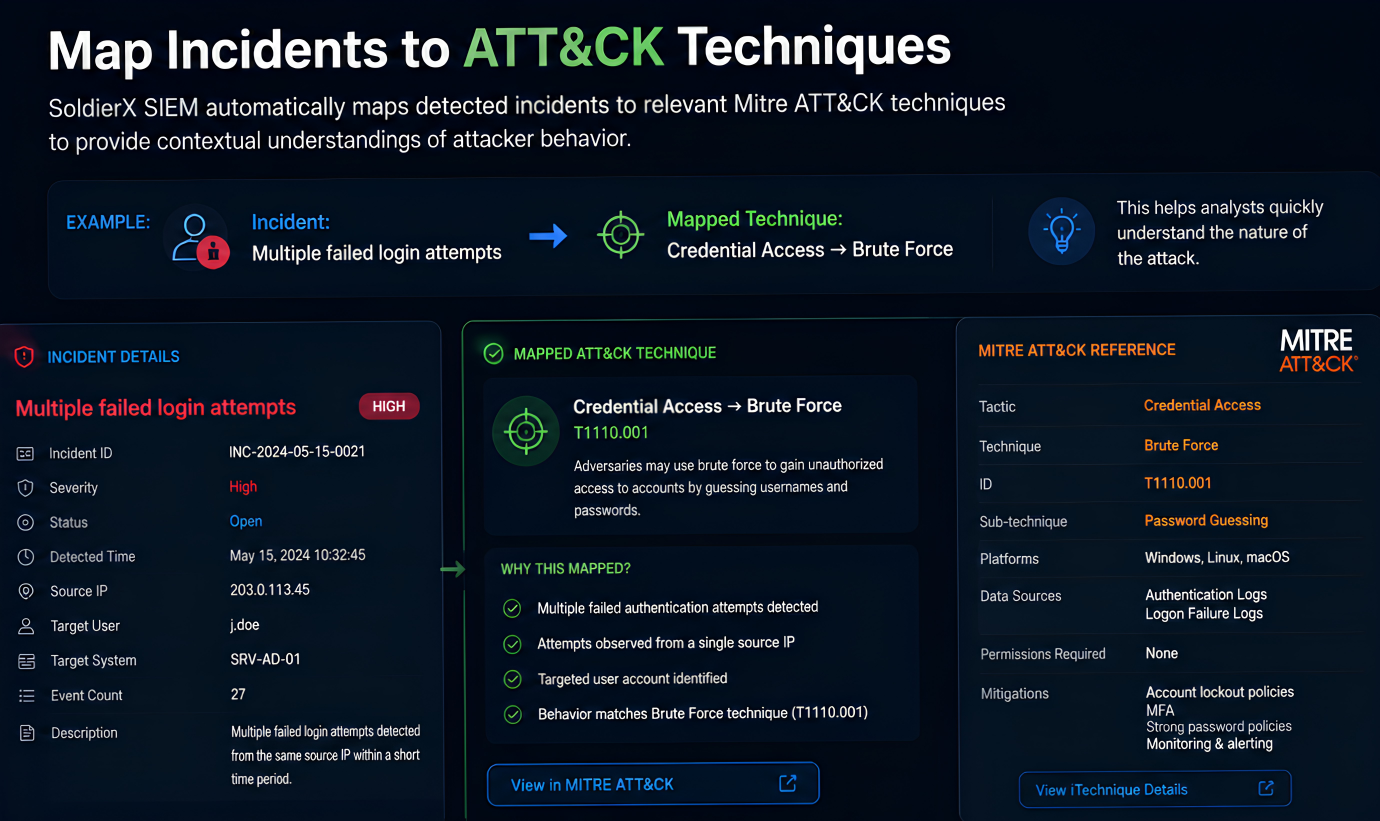
1. Map Incidents to ATT&CK Techniques
SoldierX AI SIEM automatically maps detected incidents to relevant MITRE ATT&CK techniques to provide contextual understandings of attacker behavior.
This helps analysts quickly understand the nature of the attack.
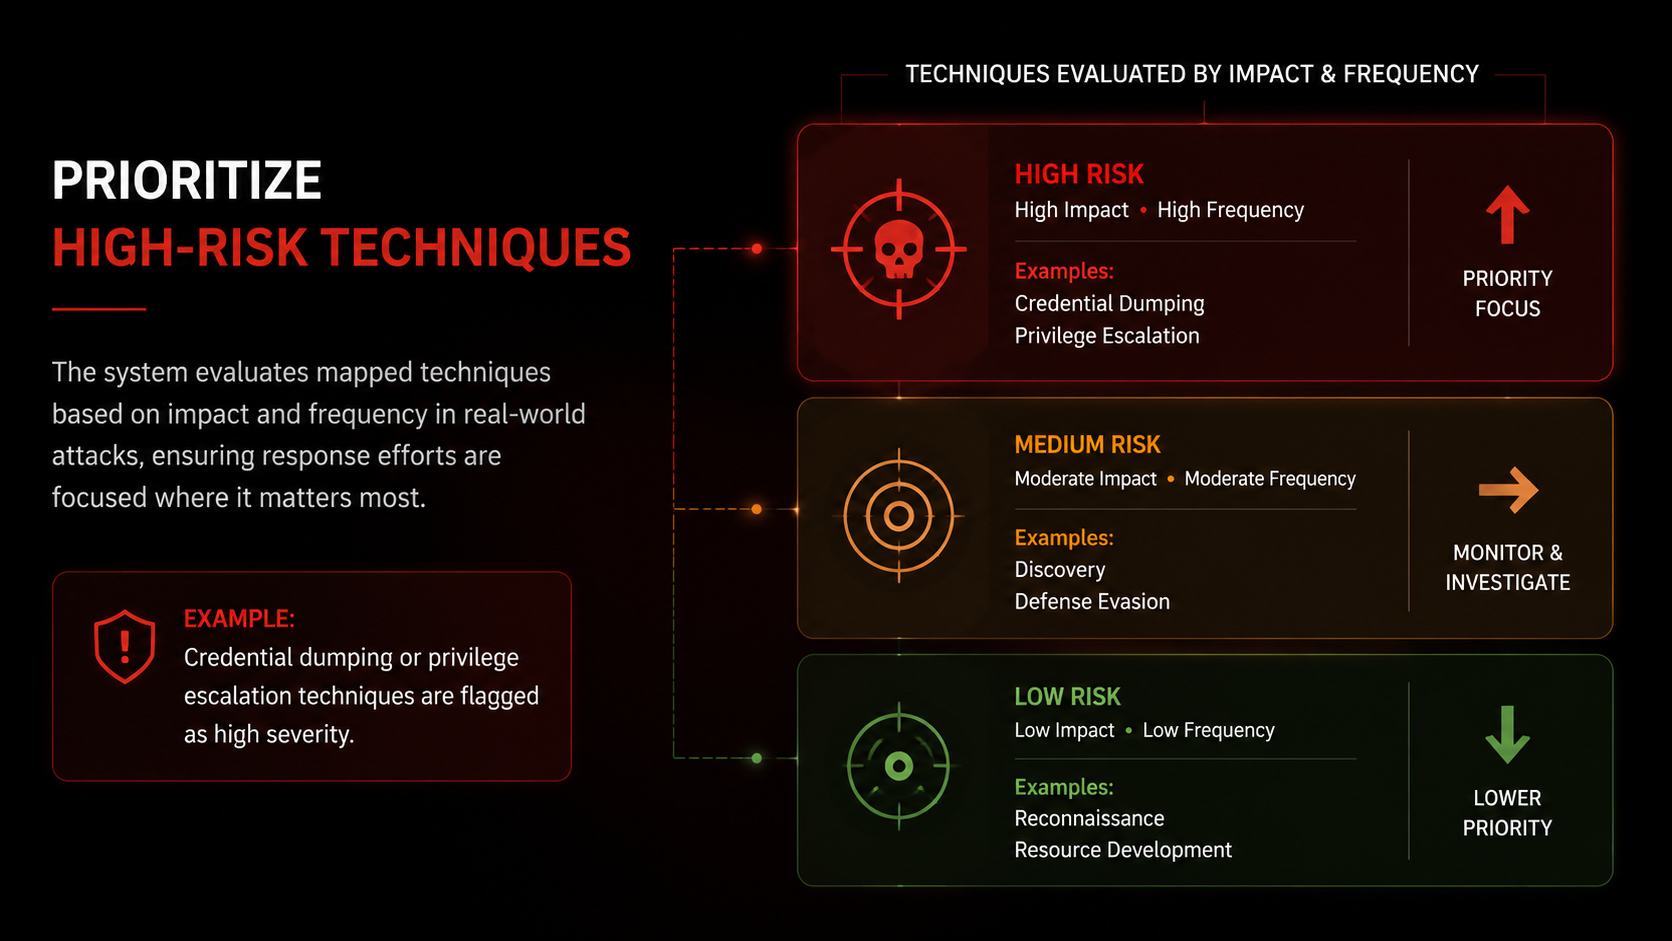
2. Prioritize High-Risk Techniques
The system evaluates mapped techniques based on impact and frequency in real-world attacks, ensuring response efforts are focused where they matter most.
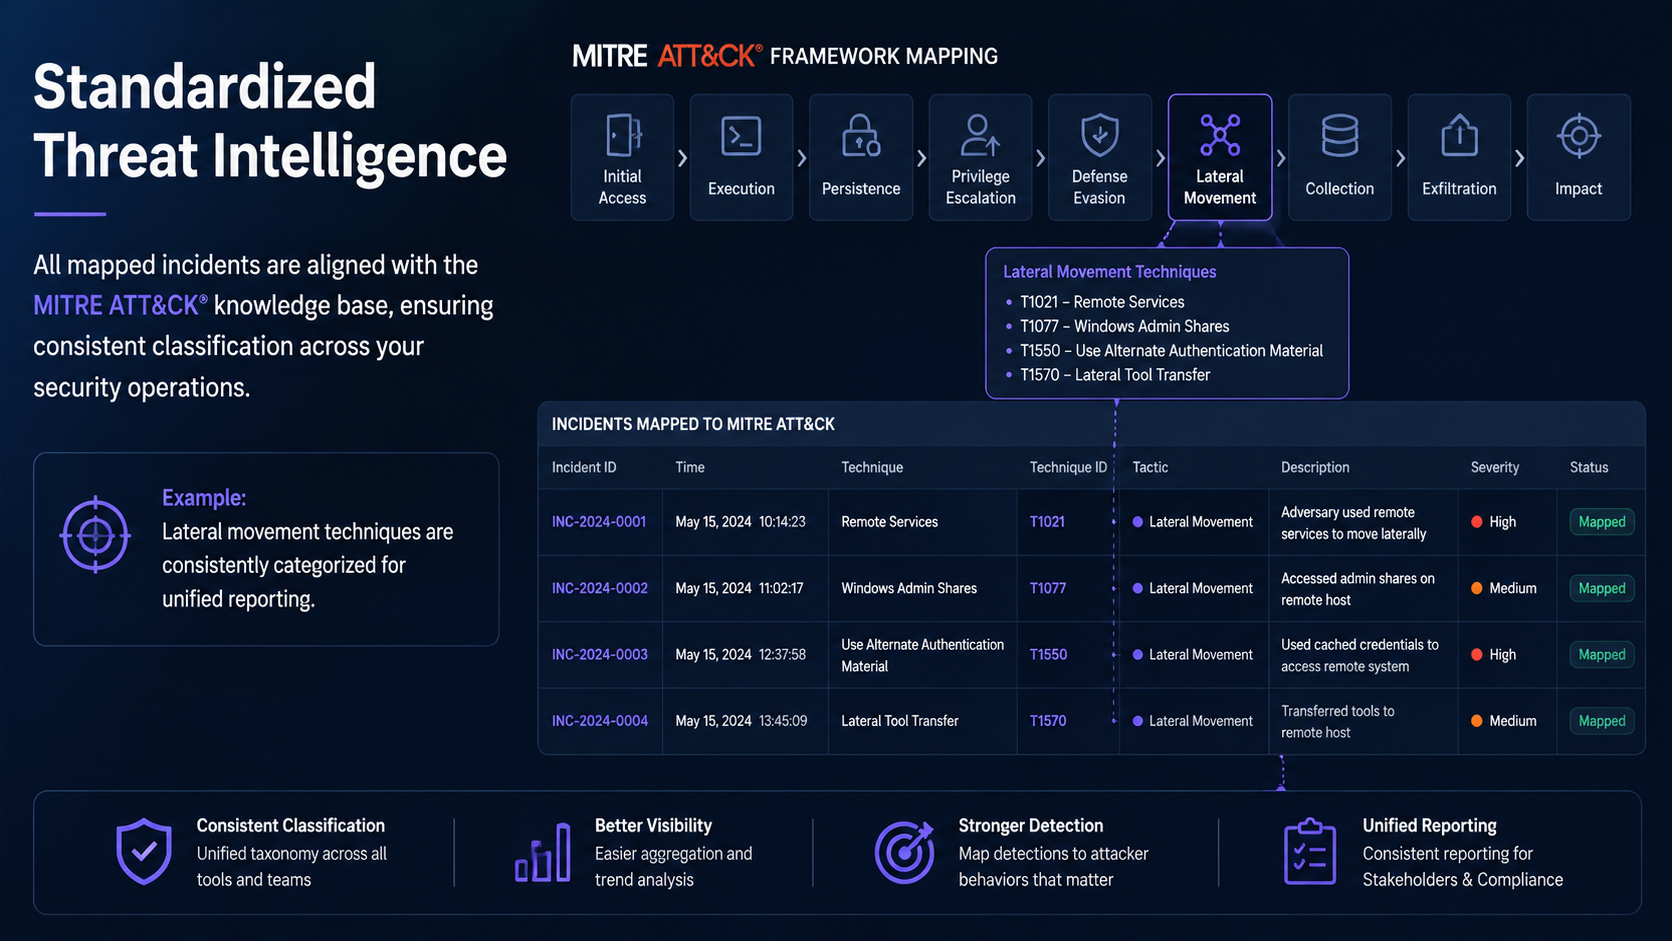
3. Standardized Threat Intelligence
All mapped incidents are aligned with the MITRE ATT&CK knowledge base, ensuring consistent classification across your security operations.
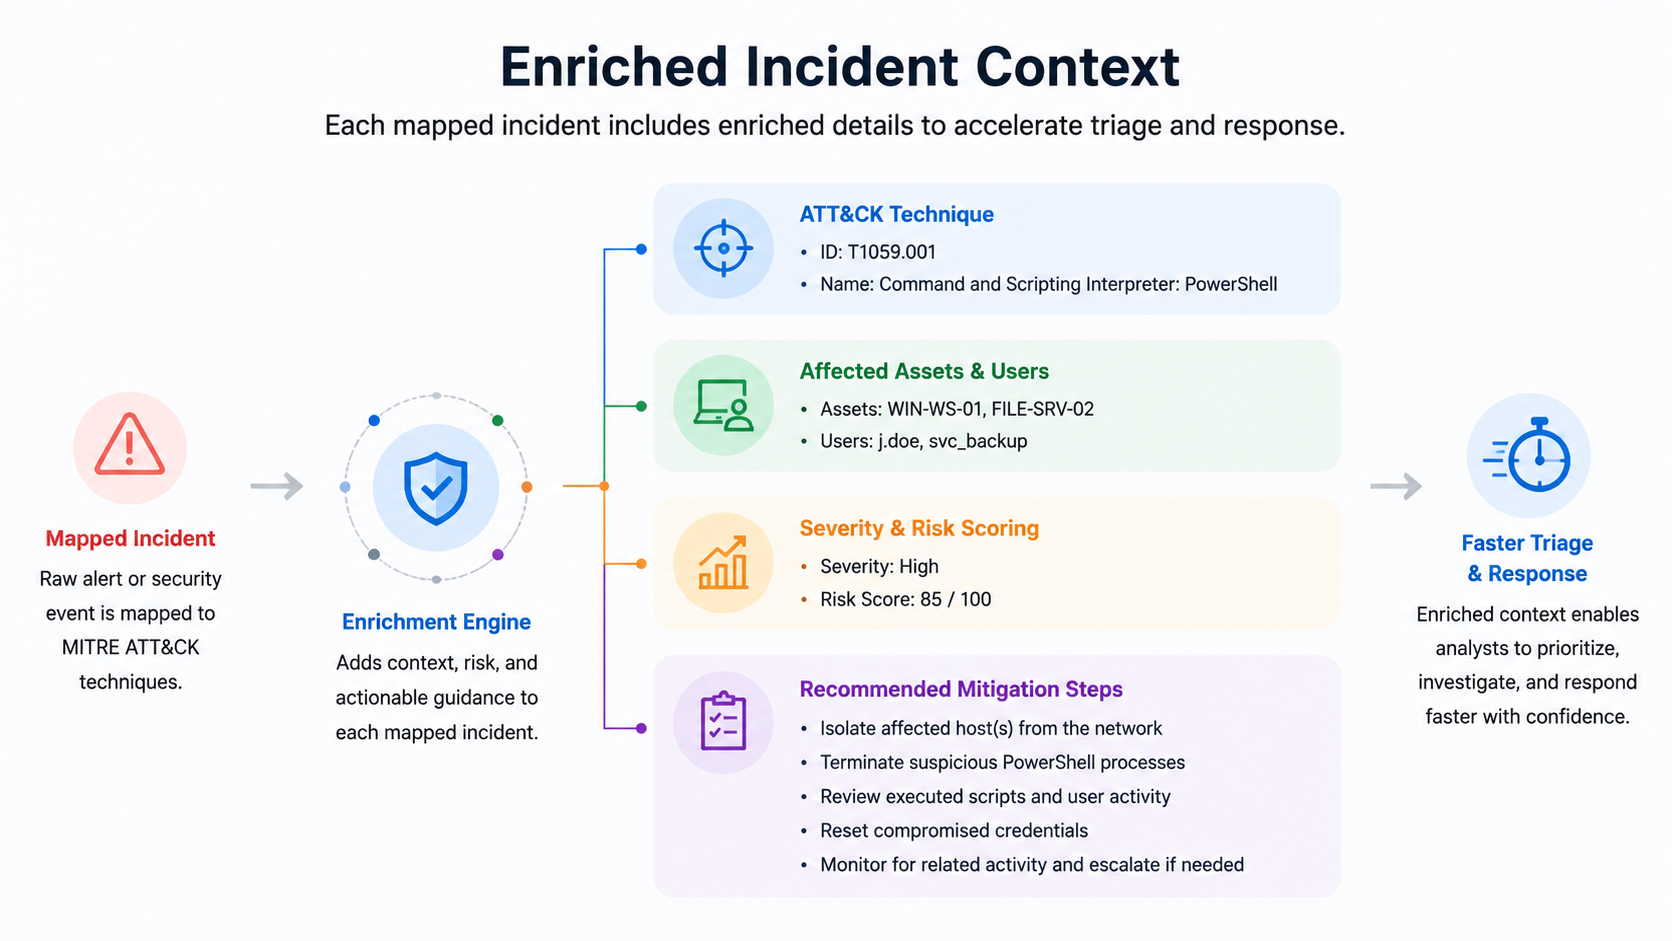
4. Enriched Incident Context
Each mapped incident includes enriched details such as:
This enables faster triage and response.
Use Cases
Map incidents to MITRE ATT&CK techniques to gain insights into attacker tactics, such as credential harvesting or lateral movement.
Prioritize Responses
Focus on high-risk techniques by identifying their impact and prevalence in real-world attacks.
Align with Industry Standards
Use the MITRE ATT&CK framework to standardize your incident analysis and demonstrate alignment with global best practices.
Threat Hunting
Search for indicators of compromise (IOCs) based on MITRE ATT&CK techniques to proactively uncover hidden threats.
Why Choose
SoldierX AI SIEM
for MITRE ATT&CK Mapping?
Gain deep visibility into attacker behavior and align your incident response with global cybersecurity standards. AI anomaly detection adds context for behavior that does not match a known technique.
Actionable Insights
Map incidents to specific MITRE ATT&CK techniques for deeper understanding and faster response.
Industry Alignment
Leverage the globally recognized MITRE ATT&CK framework to standardize your incident analysis.
Prioritized Responses
Focus on high-risk techniques by identifying their impact and prevalence in real-world attacks.
Comprehensive Coverage
Cover all stages of an attack lifecycle, from initial access to exfiltration.
Threat Intelligence Integration
Enrich incidents with context from the MITRE ATT&CK knowledge base.
Beyond Known Techniques
AI anomaly detection complements MITRE ATT&CK mapping by flagging behavior that fits no known pattern.