

Powerful Features for Modern Security Teams
SoldierX AI SIEM combines threat detection, centralized log management and AI-driven analytics in a single platform. Whether you monitor access patterns, analyze traffic or track server health, every feature is built to simplify security.

Real-Time Threat Detection
Stay ahead of attackers with continuous monitoring and instant alerts.
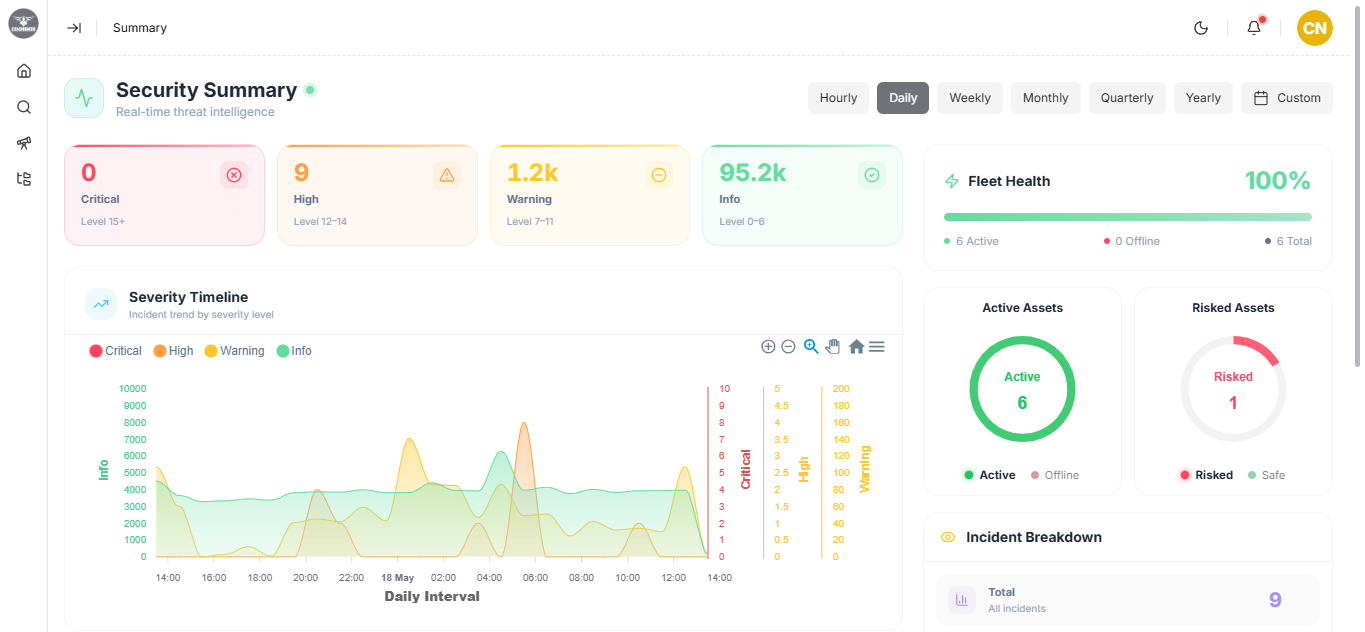
- Detect unauthorized access, brute-force attacks, and DoS (Denial of Service) in timely fashion using log analysis.
- Instant notifications via email or in app.
AI-Powered Anomaly Detection
Catch threats your environment has never seen before, using two independent AI engines.
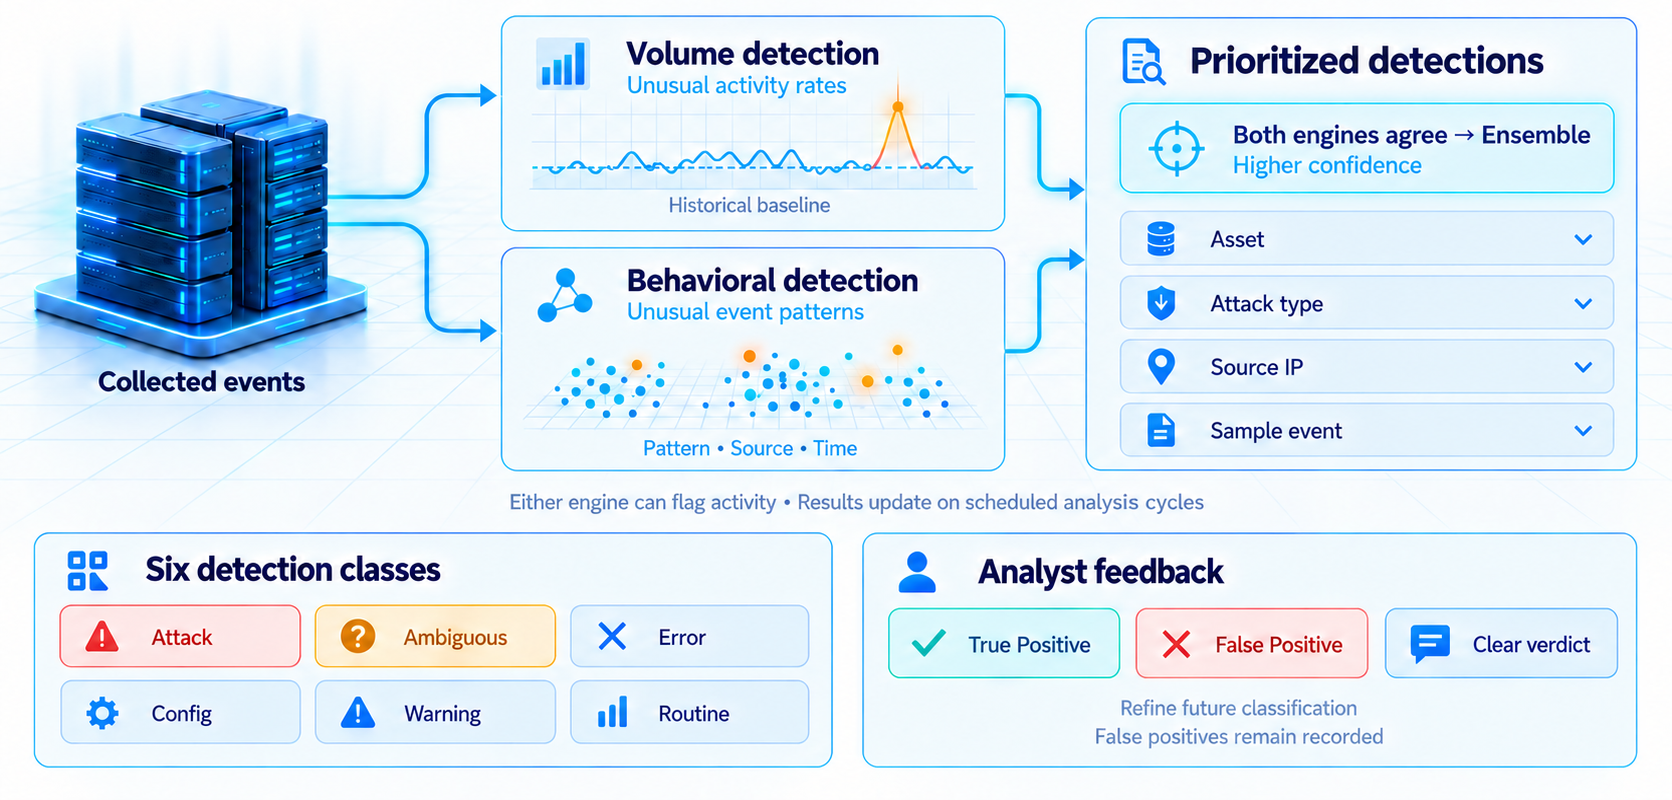
- Volume-based detection flags activity that breaks your environment's own historical baseline.
- Behavioral detection scores every event for outliers against normal patterns.
- Ensemble confidence scoring when both engines agree, plus a six-class triage system so nothing real gets buried.
Advanced Log Analysis
Go beyond raw logs with intelligent analytics.
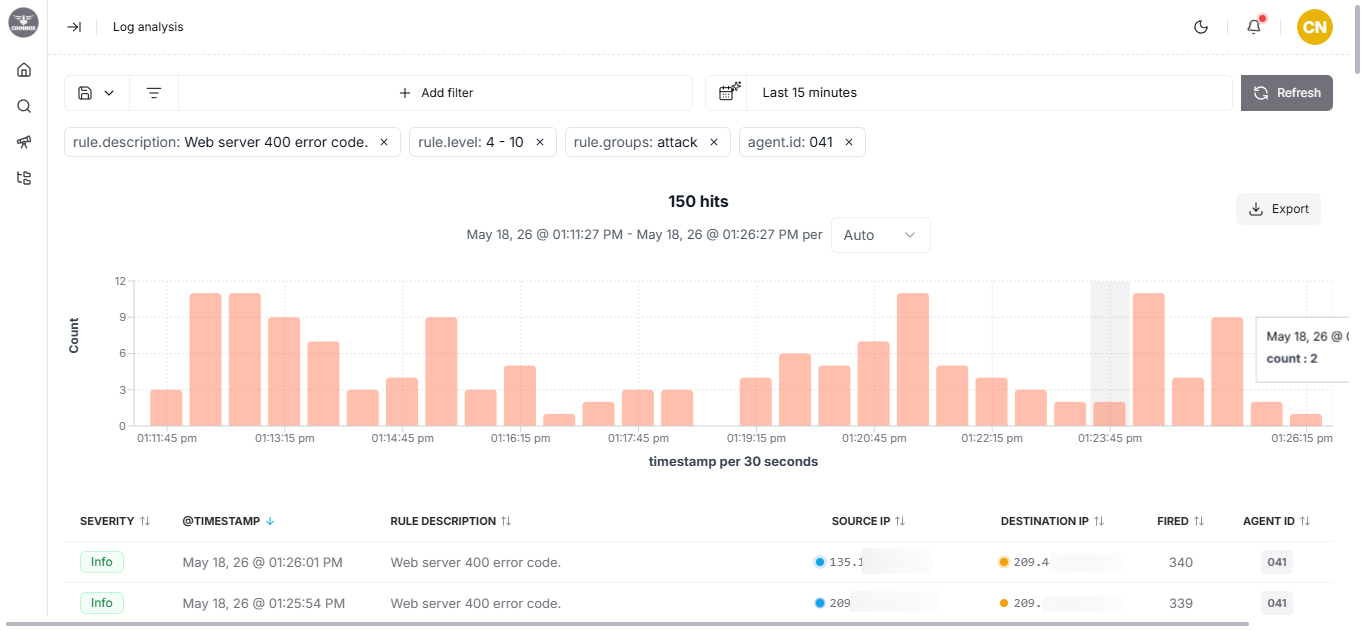
- Parsing of log data to detect anomalies with Log Analysis module
- Behavioral anomaly detection for zero-day threats.
- Correlate events to uncover attack patterns (e.g., failed logins → breach) using Incidents Correlation.
Actionable Insights & Alerts
Respond faster with enriched, context-rich alerts.
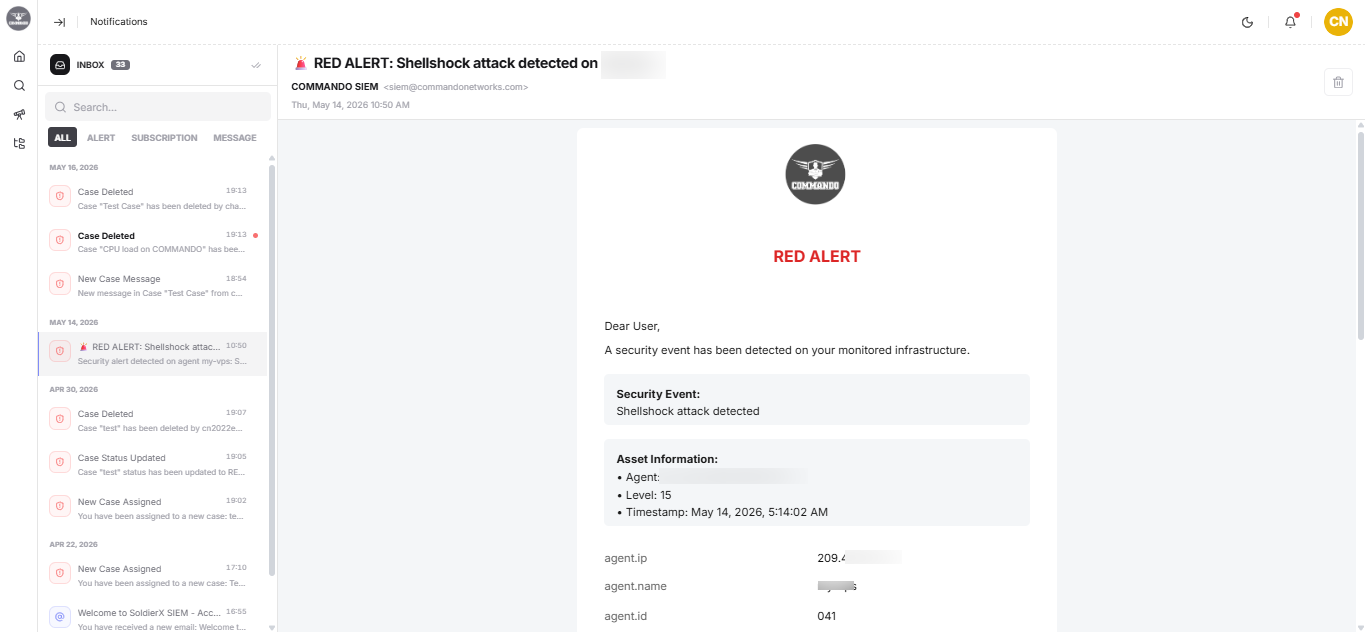
- Alerts include source IP, target asset, user, and severity.
- Link related incidents into a single case using Incidents Correlation.
- One-click drill-down for full investigation.
Personalized Alerts
Stay informed about what matters with SoldierX AI SIEM.
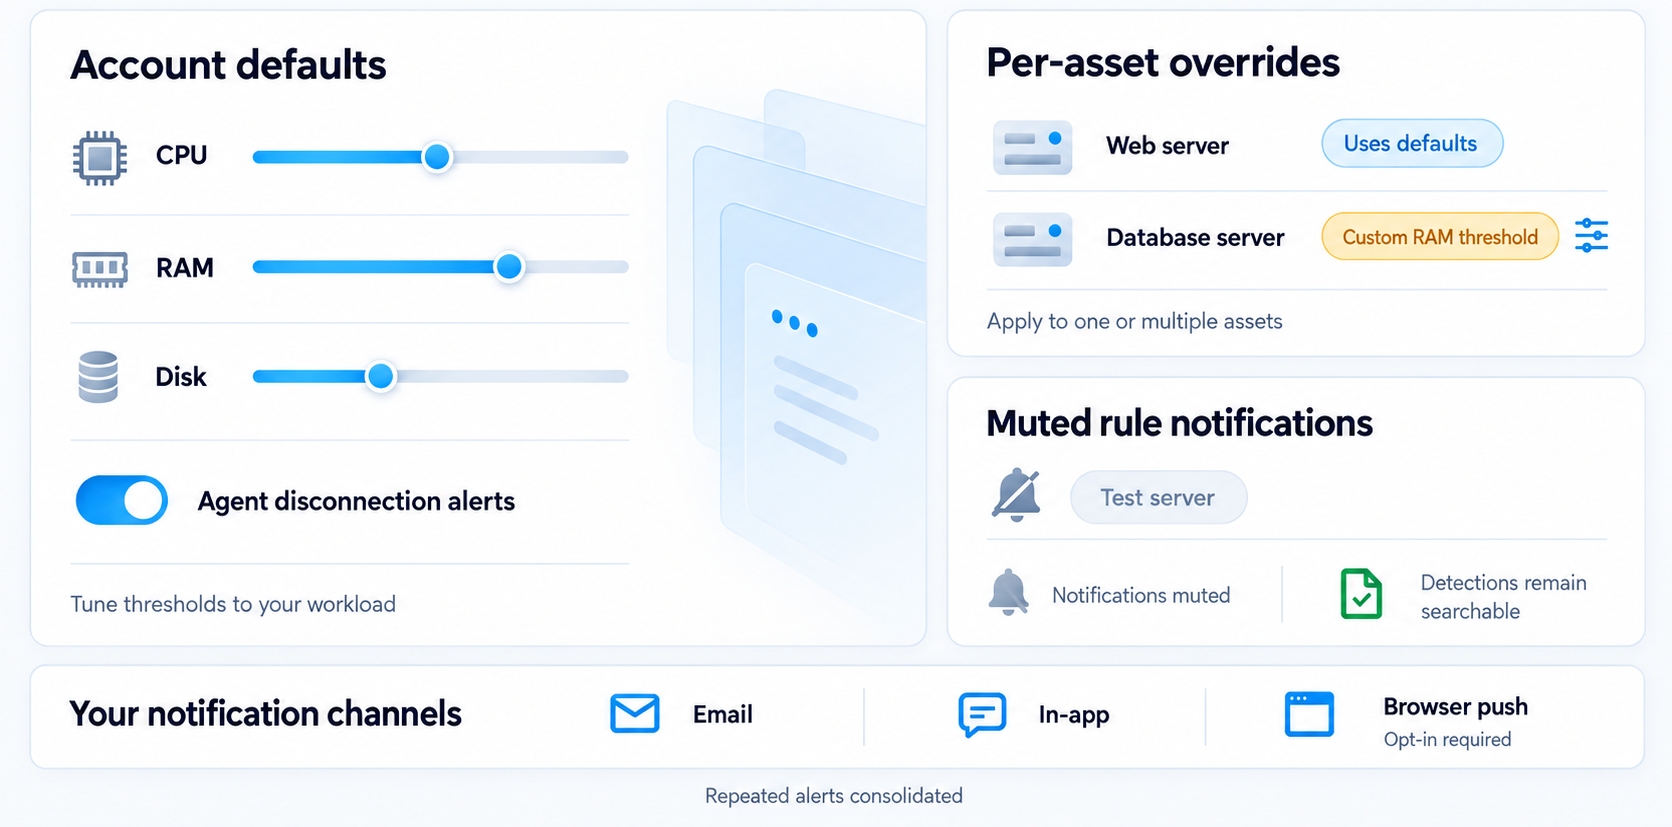
- Tune CPU, RAM, disk, and disconnection alerts with account defaults and per-asset overrides.
- Mute noisy rule notifications while keeping every detection logged and searchable.
- Receive updates through email, timely in-app notifications, and browser push alerts.
Incident & Case Management
Streamline investigations and resolve incidents efficiently.
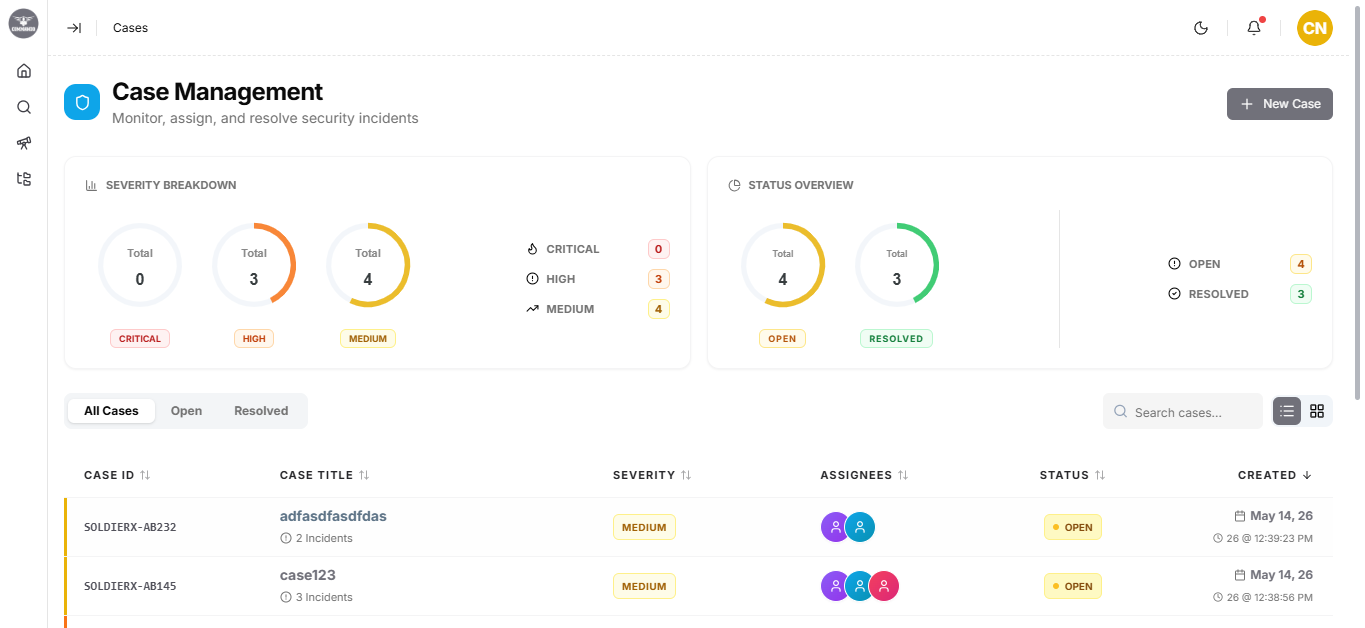
- Group related incidents into cases for streamlined workflows using Case Management.
- Assign, track progress, and collaborate with your team.
- Timeline view powered by Incidents Correlation to visualize attack patterns.
In-Depth IP Analysis
Uncover hidden risks with actionable intelligence.
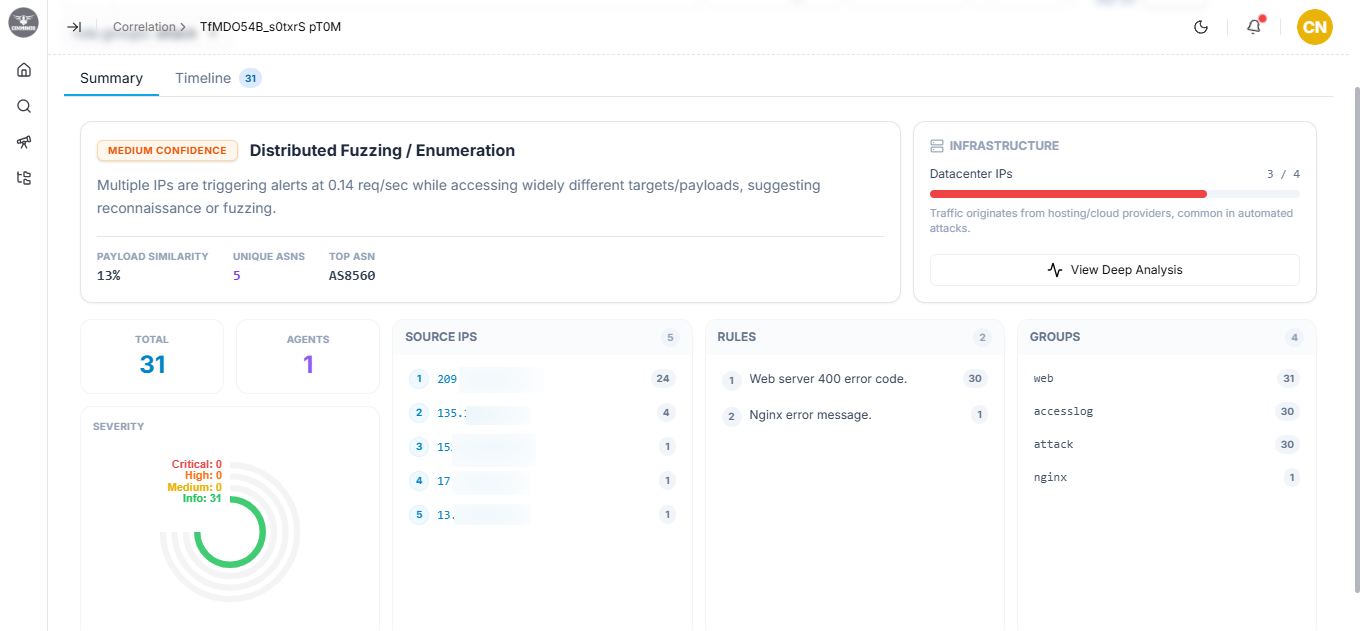
- Analyze suspicious IPs with scam scores, ISP details, geolocation, and historical activity.
- Use In-Depth IP Analysis to identify and mitigate threats before they escalate.
MITRE ATT&CK Mapping
Understand attacker behavior with industry-standard insights.
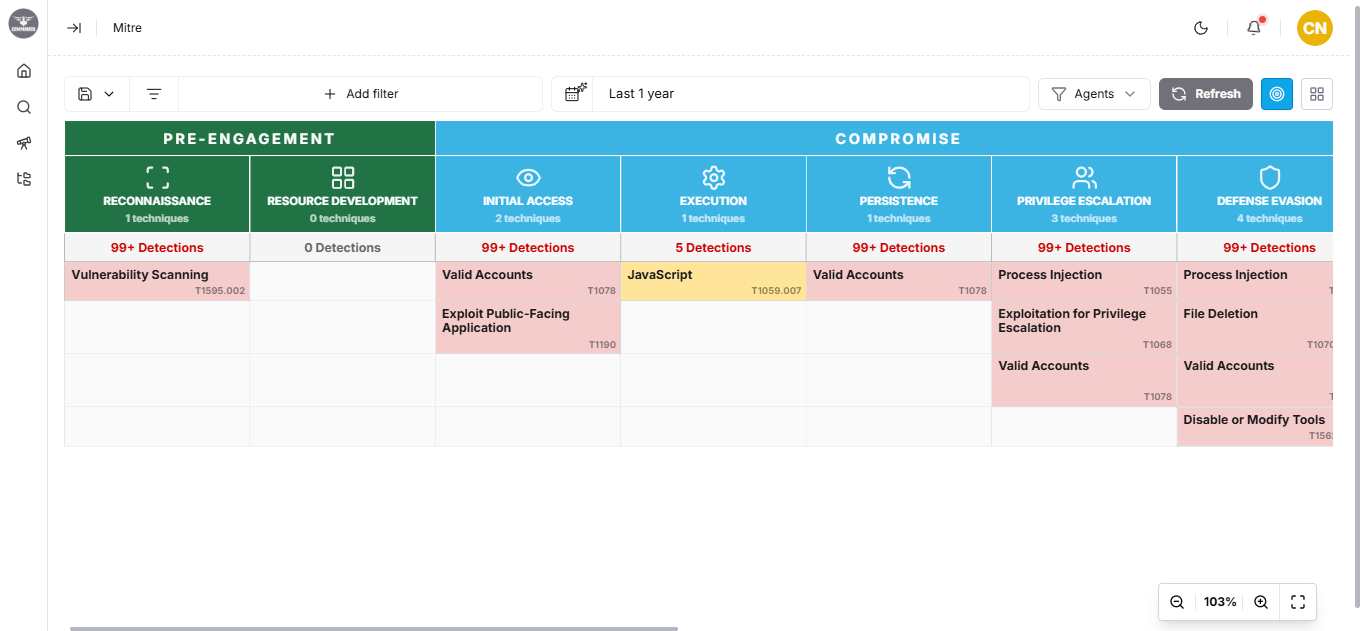
- Map detected incidents to the MITRE ATT&CK framework for actionable intelligence.
- Identify attack techniques (e.g., "Credential Access" → "Brute Force") and prioritize responses.
Centralized Log Management
Eliminate silos with a single source of truth for all your logs.
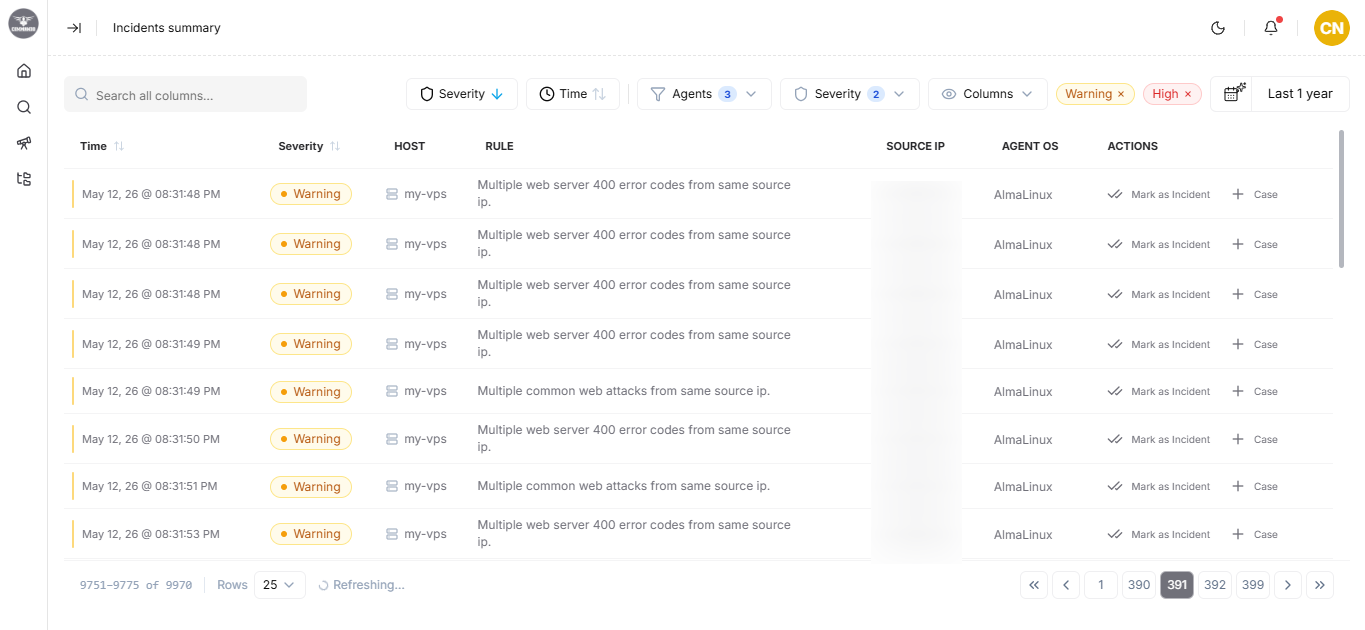
- Lightweight SIEM agent collects logs from servers, and endpoints, Agent timely Analysis.
- Searchable archives for audits and forensic investigations.
Agentless Connectivity
Monitor devices that can't run software of their own.
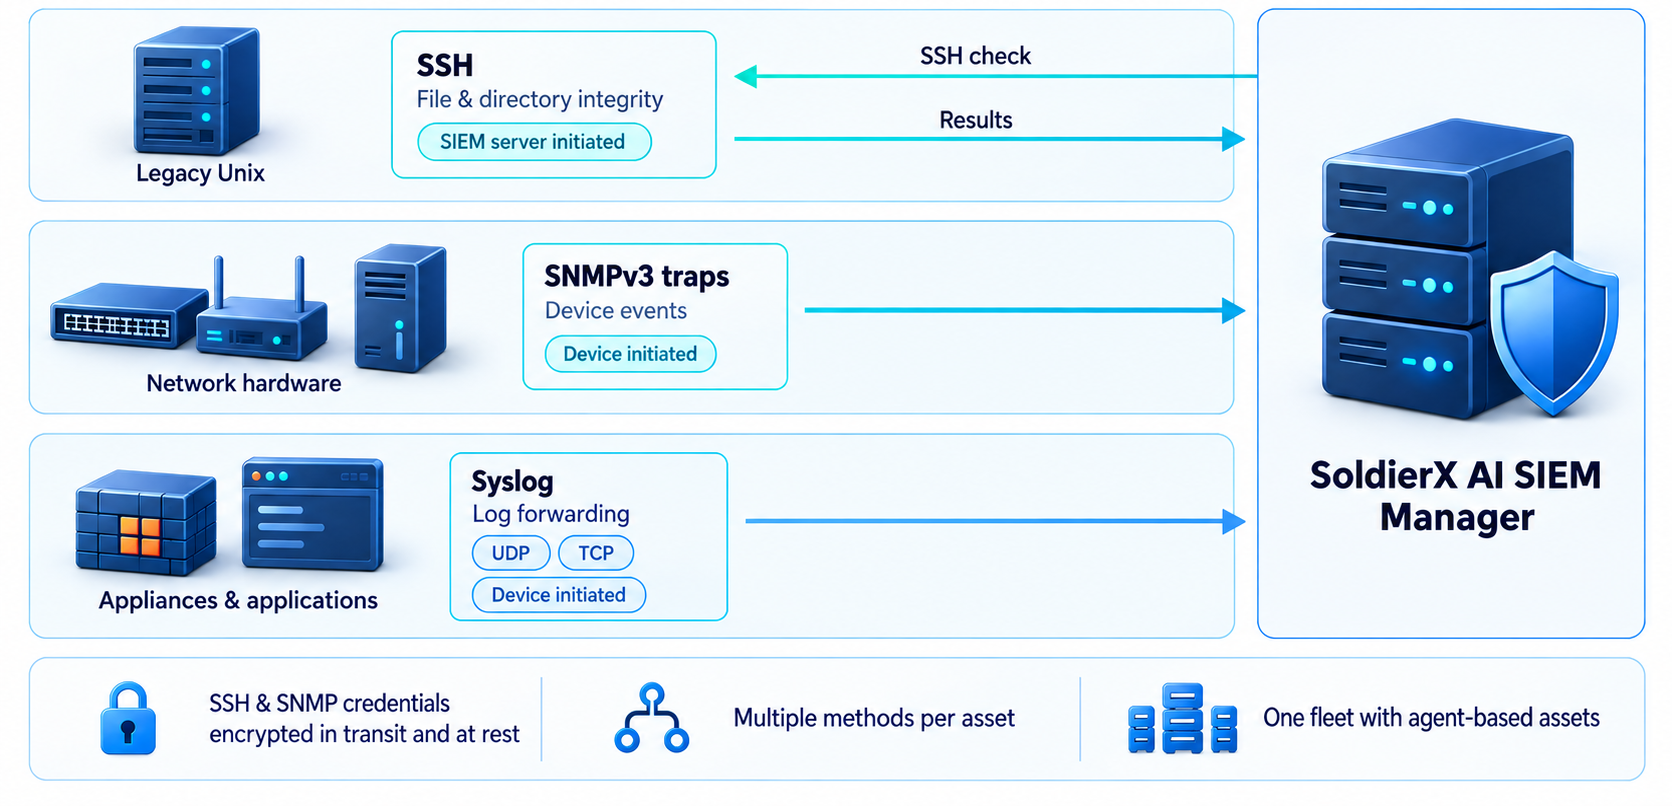
- Connect firewalls, routers, and legacy systems via SSH, SNMP trap, or Syslog forwarding, no install required.
- Encrypted credential storage for every agentless connection method.
- Mix agent-based and agentless assets in the same fleet.
Multi-Asset Monitoring
Gain full visibility across your infrastructure.
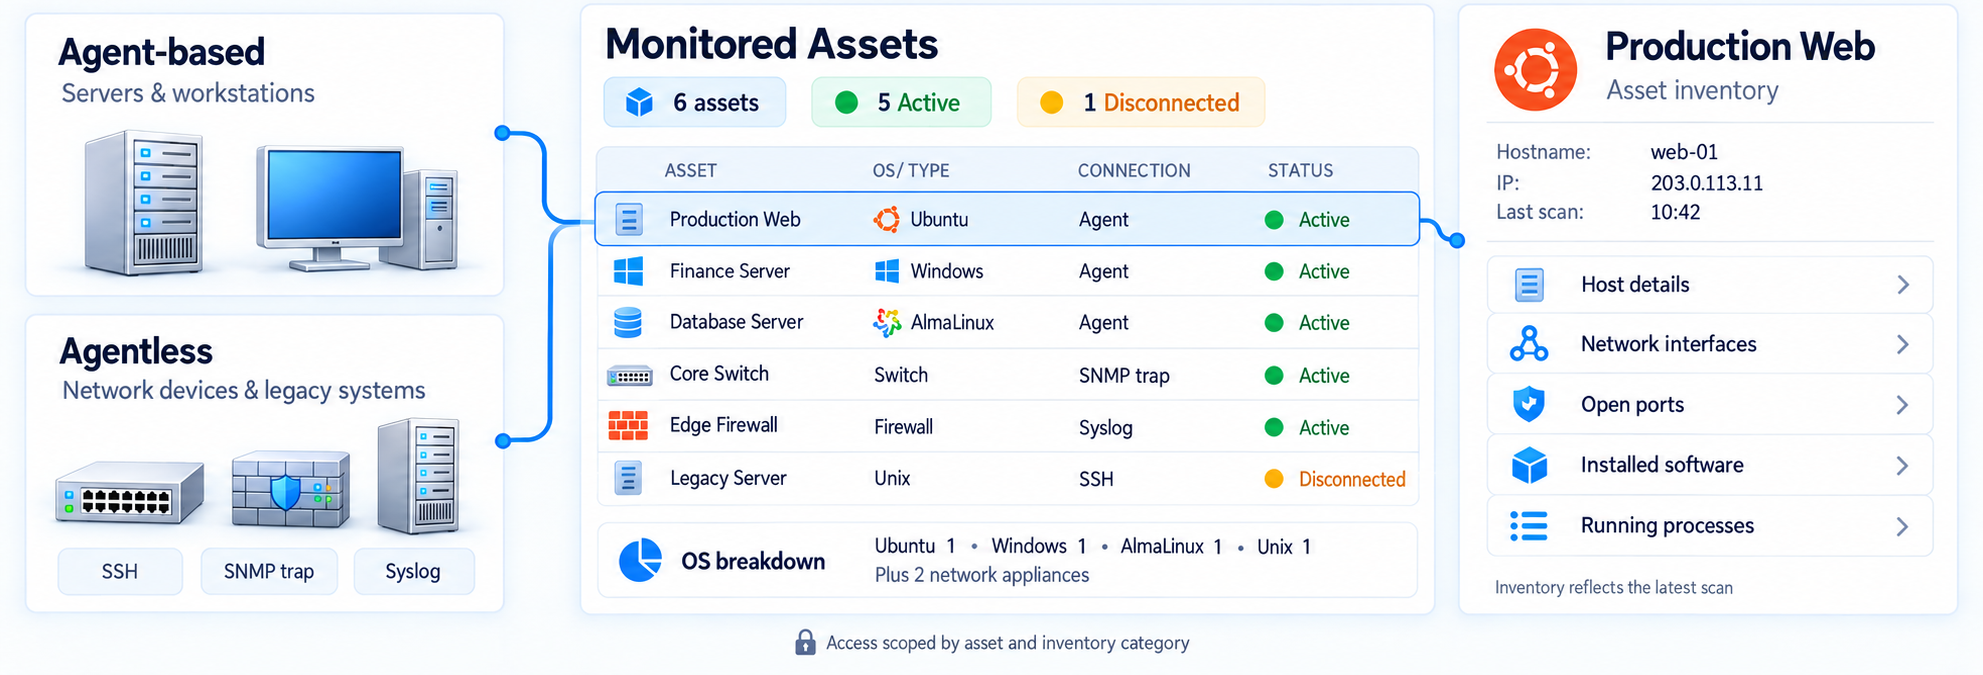
- Monitor servers, endpoints, VPS, and more with Agent Realtime Analysis.
- Drill down into individual assets for detailed metrics, including installed packages, running processes, and open ports.
Server Health Monitoring
Ensure optimal performance and detect system-level threats.
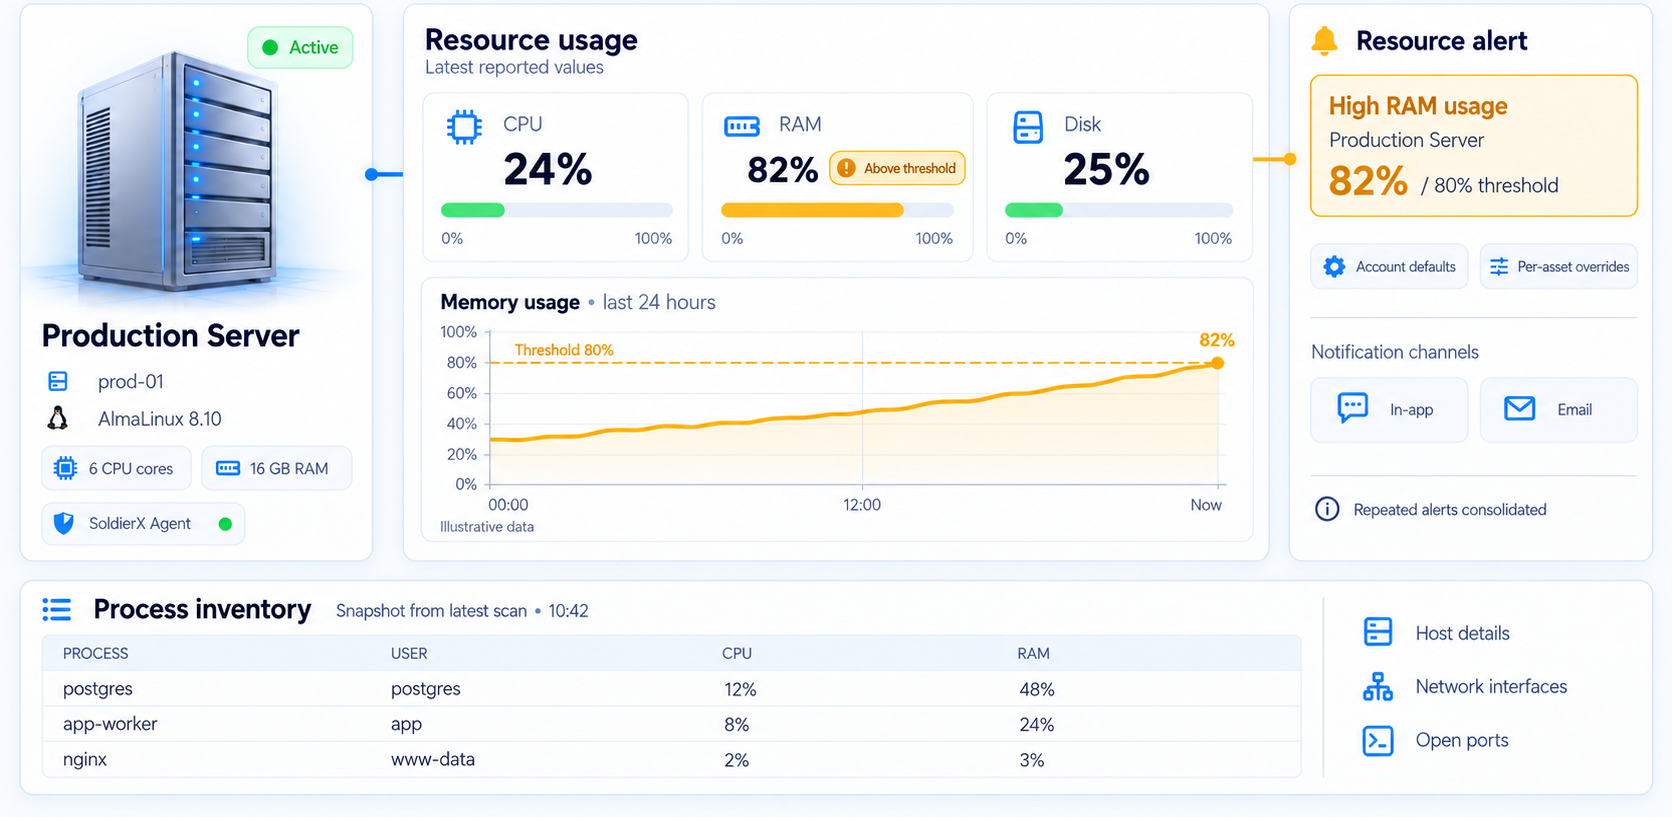
- Real-time CPU, RAM, disk usage and more tracking with Agent Realtime Analysis.
- Alerts for high usage or unusual activity.
Identity & Access Management
Enterprise-grade, granular access control for every team member.
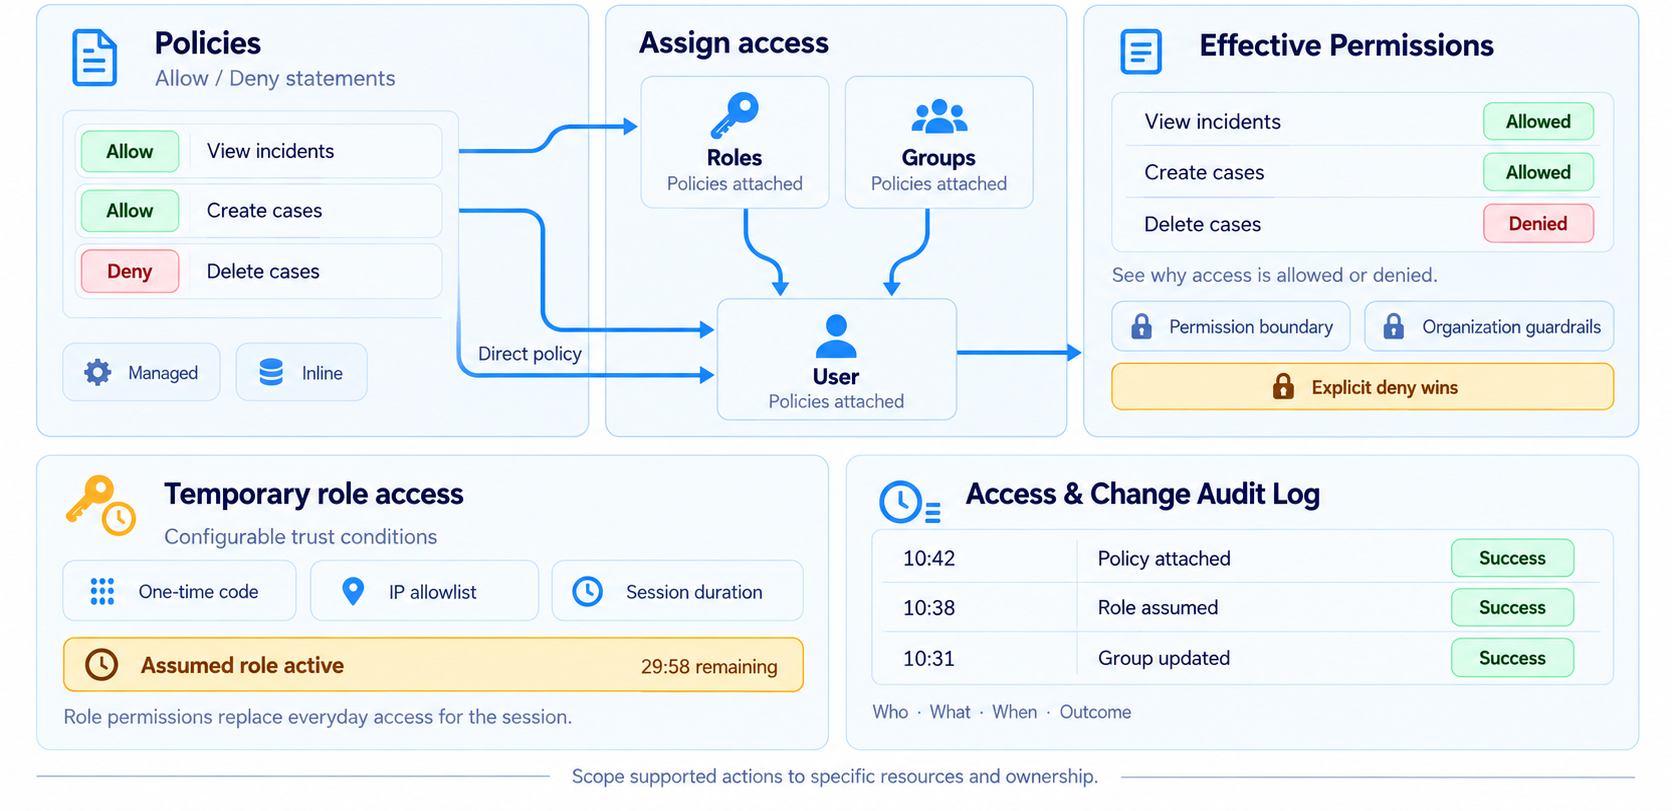
- Build precise policies from reusable actions, assigned through roles and groups.
- Grant temporary elevated access with assumable roles, verification codes, and IP allowlists.
- See exactly why any permission is granted or denied with the Effective Permissions inspector, backed by a complete audit trail.
Intuitive & Customizable Workspaces
Turn complex data into clear, actionable insights.
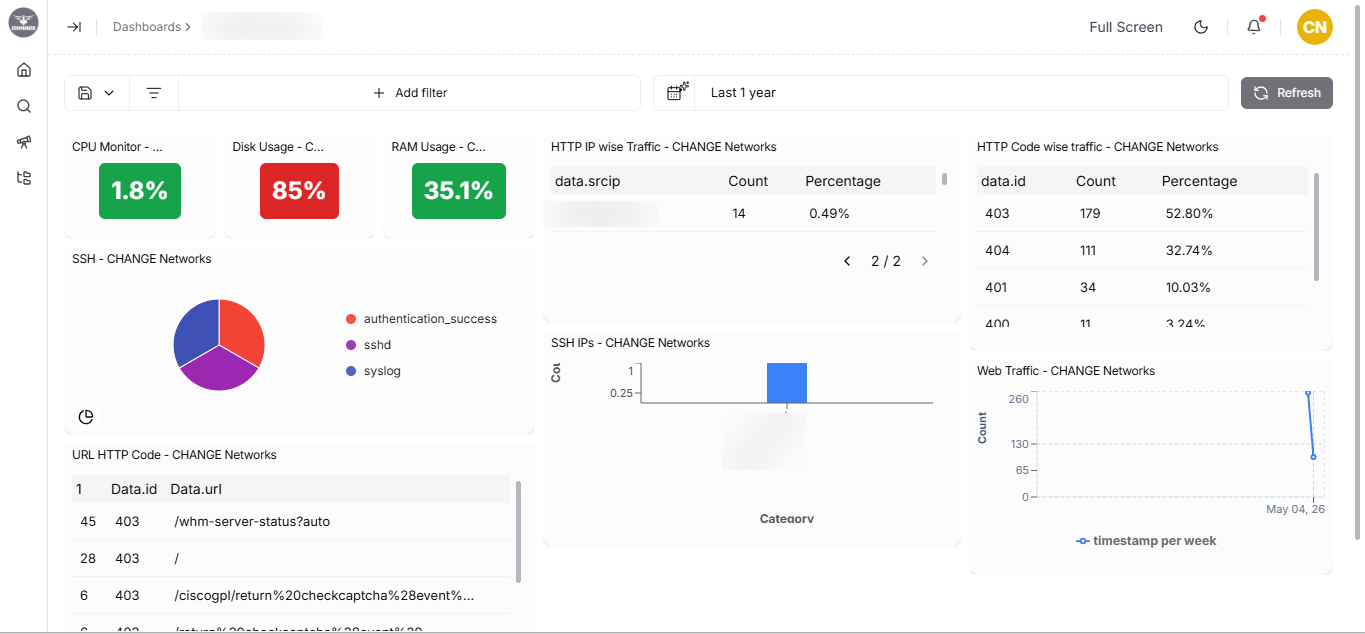
- Dynamic widgets: pie charts, bar graphs, metrics, line charts powered by log data.
- Fully customizable workspaces for easy monitoring using Workspace Creation.
- Monitor access attempts, CPU usage, traffic trends, and more all on one screen.
Customizable Filters
Focus on what matters with precision filtering.
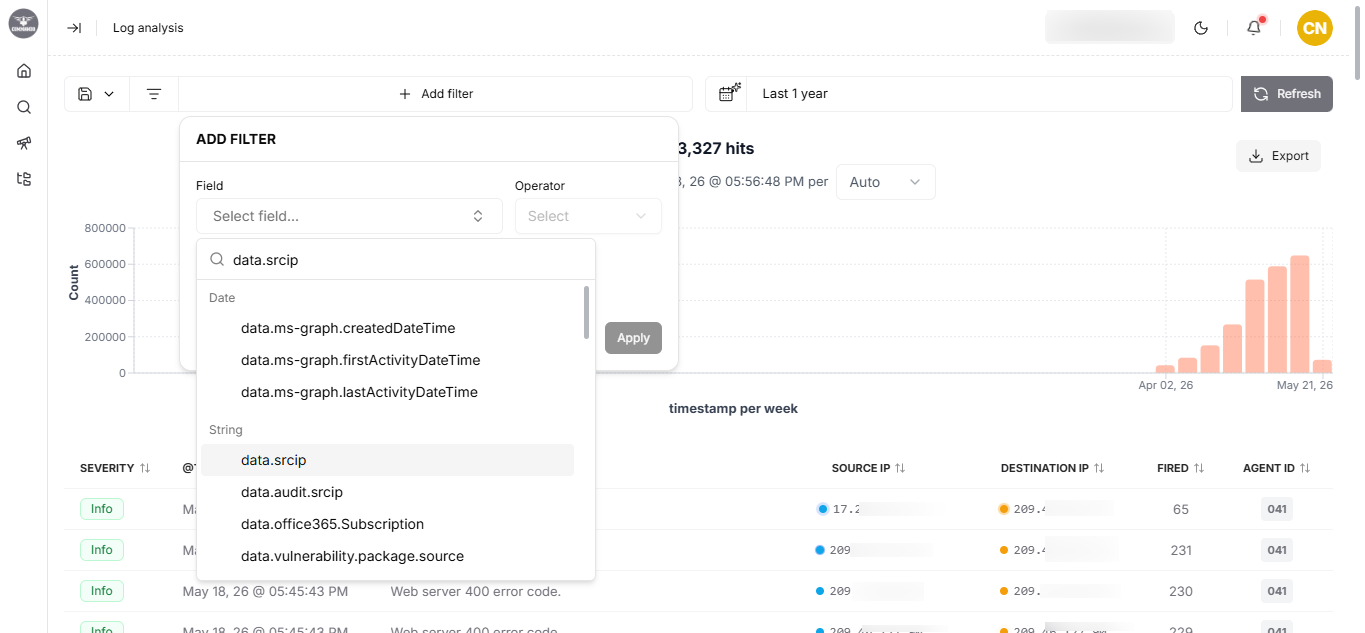
- Filter by IP, URL, response code (4xx, 5xx), user, time range, and more.
- Save filters for recurring investigations.
- Exclude noise to reduce false positives.
Scalable Architecture
Built to grow with your organization.
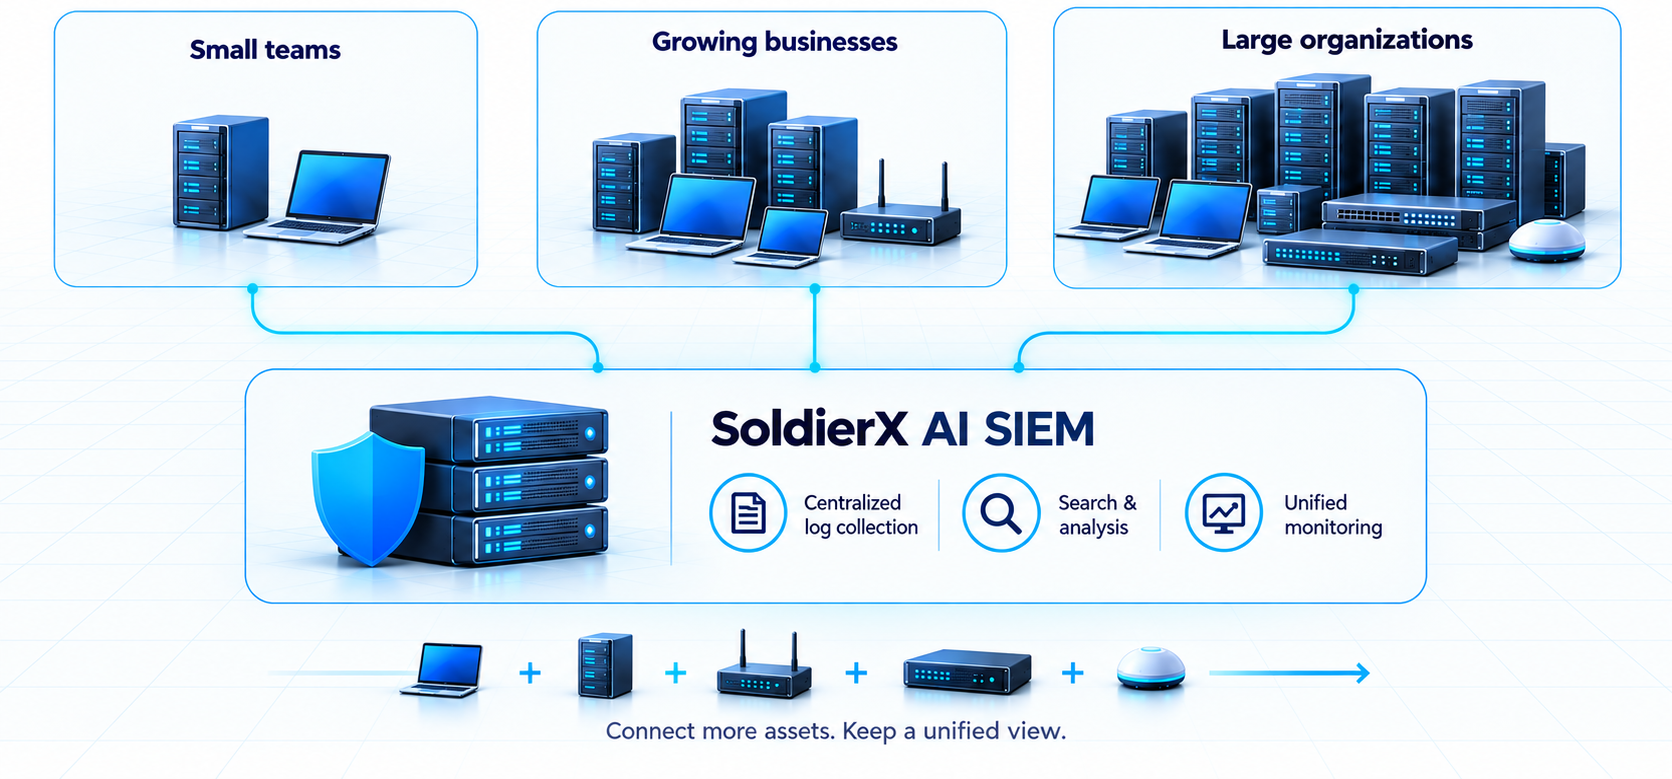
- Handles unlimited log volume without performance loss.
- Ideal for small businesses to large enterprises.