

Granular Access Control with SoldierX AI SIEM
As a security team grows, so does the risk of someone holding access they no longer need, or never should have had. Built on zero trust and least-privilege principles, SoldierX AI SIEM's Identity & Access Management gives every organization precise, predictable control over who can do what, so day-to-day permissions stay tightly scoped to what's actually needed, short-term access never outlives the task it was granted for, and every change is there to review when you need it.
Core Advantages
Key Benefits
Least-Privilege Policies
Build precise policies that grant exactly what someone needs to do their job, and nothing more, the core of least-privilege access.
Assumable Roles
Grant temporary, elevated access for exactly as long as it's needed, never left standing afterward.
Explicit-Deny Guarantee
A zero trust model where explicit deny always wins over any allow, so access stays predictable.
Complete Audit Trail
Every policy change, role assumption, and access grant is recorded and reviewable.
Process Overview
How It Works
Build Policies from Reusable Actions
A policy is a named set of specific permissions you build once, then attach wherever it's needed. Author policies as:
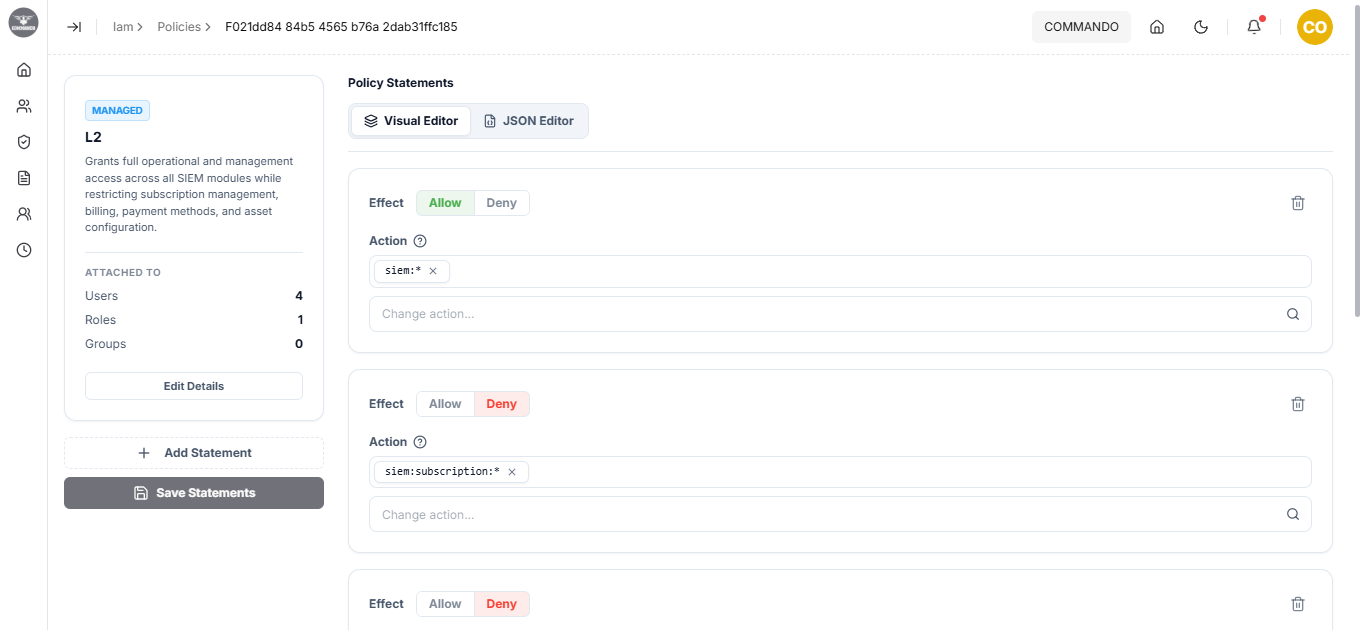
Assign via Roles & Groups
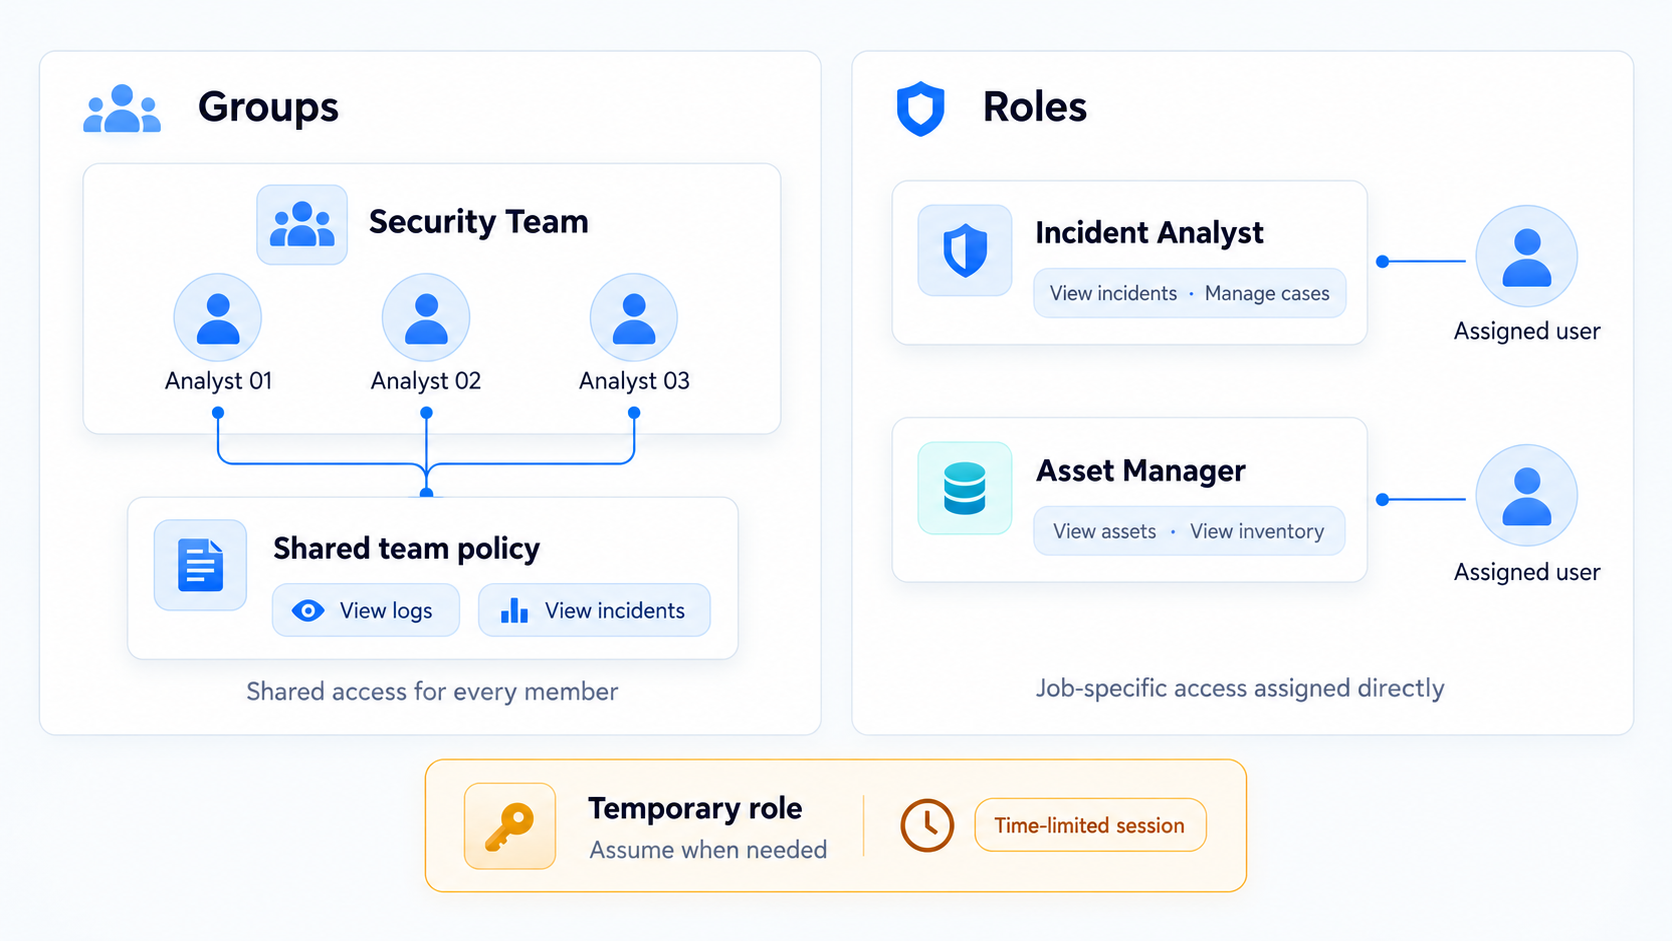
Groups mirror how your organization is already structured, so a department or team's access can be set up once and shared automatically with everyone who's part of it. Roles define what a specific job actually requires, assigned directly to the people doing that job.
Some roles can also be picked up temporarily, for situations that call for more access than someone's everyday permissions cover.
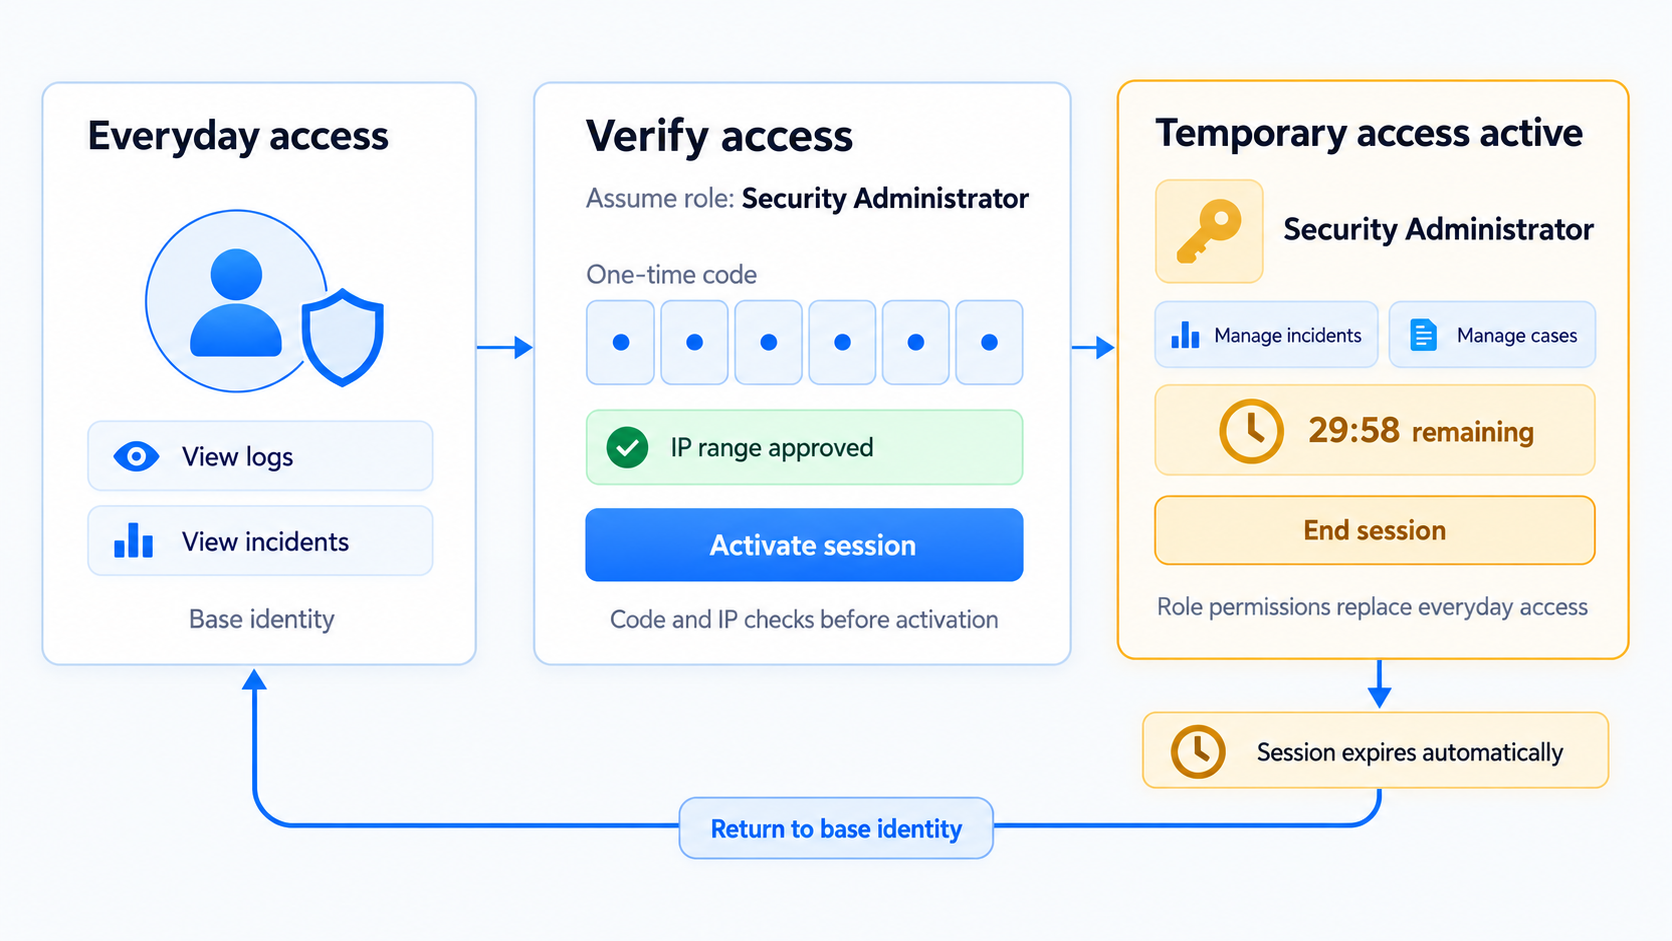
Assumable Roles for Temporary Access
For sensitive operations that shouldn't be part of anyone's everyday access, an assumable role lets someone step into elevated permissions for a bounded session:
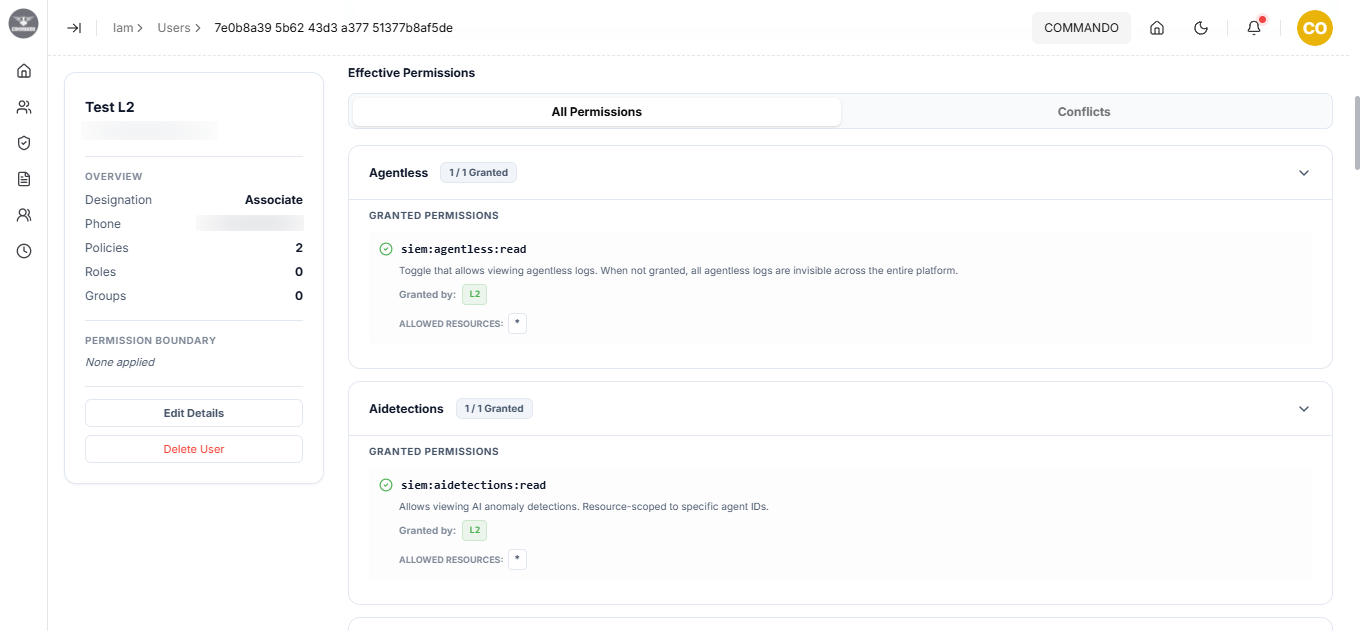
Verify with the Effective Permissions Inspector
See, module by module, exactly what any user can and can't do, and the specific reason why:
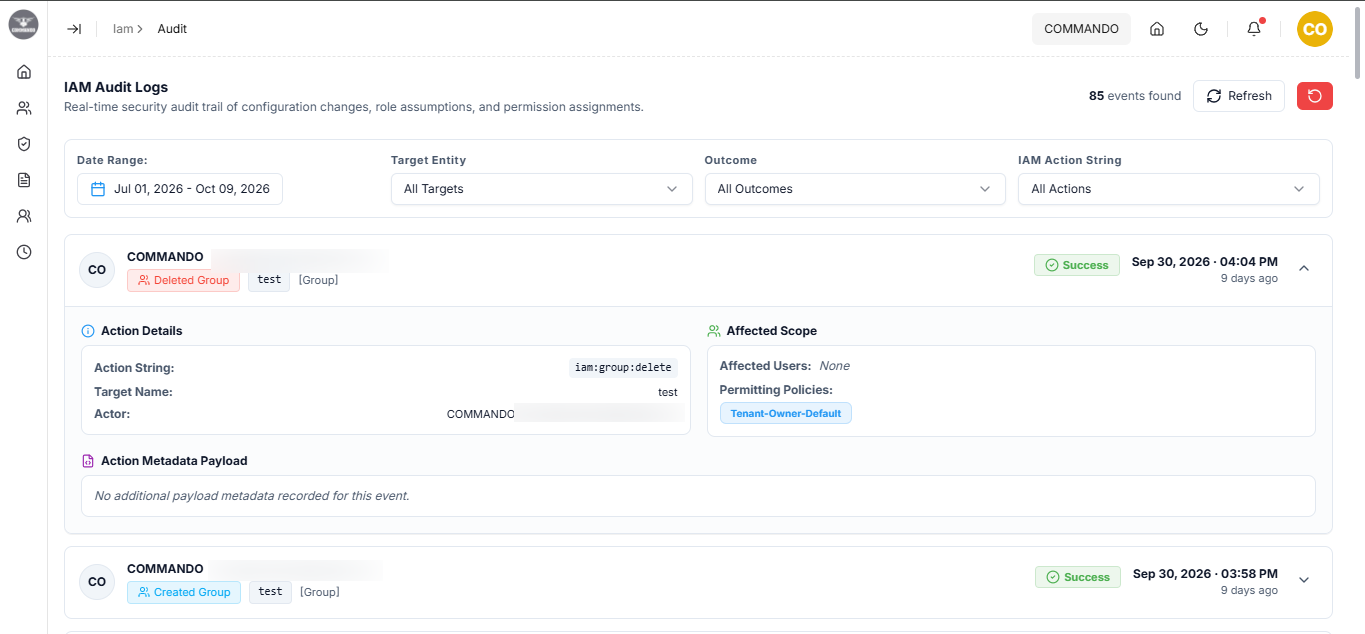
Track Everything in the Audit Log
Every policy change, role assumption, and identity switch is recorded, building a clean, searchable history of exactly who had what access, when.
Everything you need for a compliance review, without reconstructing history by hand.
Use Cases
Give every team member exactly the access their role requires, no more, no less.
Least-Privilege Team Onboarding
Start every new team member on a narrow, purpose-built role and expand access only as their real responsibilities grow, keeping least privilege intact from day one.
Temporary Incident-Response Access
Grant a responder exactly the elevated permissions a serious incident requires, for a bounded session, with zero standing access left behind.
Compliance-Ready Access Reviews
Pull a complete, timestamped record of every access change for an audit, with no manual reconstruction required.
Multi-Team Segmentation
Scope access down to specific assets and specific teammates, so one team's workflow never spills into another's.
Why Choose
SoldierX AI SIEM
for Access Management?
Grant exactly the right access, for exactly the right amount of time, with a complete record of every change along the way. AI anomaly detection flags activity that deviates from a user’s normal behavior.
Predictable by Design
An explicit deny always wins, so you can always reason about exactly what someone can do.
Never Over-Grant
You can never grant someone more access than you yourself hold, keeping every grant aligned with least privilege.
Precise, Two-Way Narrowing
Narrow any grant down to the exact assets or cases it should cover, and the exact people it should apply to, combined however precisely you need.
Full Visibility Before You Grant
See exactly what a policy, role, or group will grant before you attach it to anyone.
Nothing Untracked
Every meaningful access change lands in a searchable, exportable audit log.
AI-Powered Detection
AI anomaly detection flags activity that deviates from a user’s or asset’s normal behavior, helping you spot misuse of access.