

Uncover Hidden Threats with SoldierX AI SIEM’s AI Anomaly Engine
Security threats often hide within the noise of everyday activity, making them difficult to identify before they become serious incidents. SoldierX AI SIEM's AI Engine continuously analyzes your security data to uncover unusual activity, recognize emerging patterns, and surface potential threats that might otherwise go unnoticed. By turning complex security signals into clear, actionable insights, SoldierX AI SIEM helps your team detect threats earlier, investigate with greater context, and respond with confidence.
Core Advantages
Key Benefits
Dual-Engine Detection
Two independent AI engines work together to scrutinize every event, delivering layered detection and greater confidence in the threats that matter.
Ensemble Confidence Scoring
When both engines flag the same activity independently, it surfaces as an Ensemble detection, the strongest signal in the system.
Six-Class Triage System
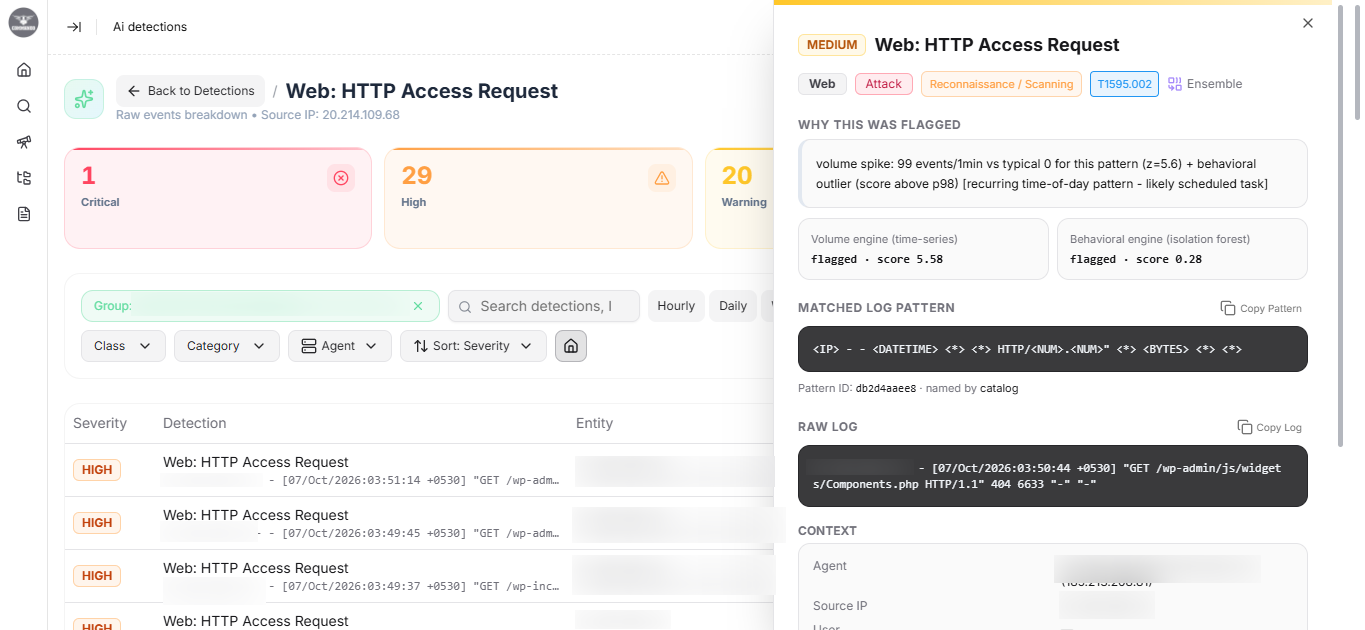
Every detection is classified as Attack, Ambiguous, Error, Config, Warning, or Routine, so real threats never get buried under operational noise.
Continuous Learning Baselines
The system learns your environment's own normal, including hour-of-day recurrence and a dedicated slow-and-steady check for brute-force and spraying attempts.
Process Overview
How It Works
Continuous Analysis
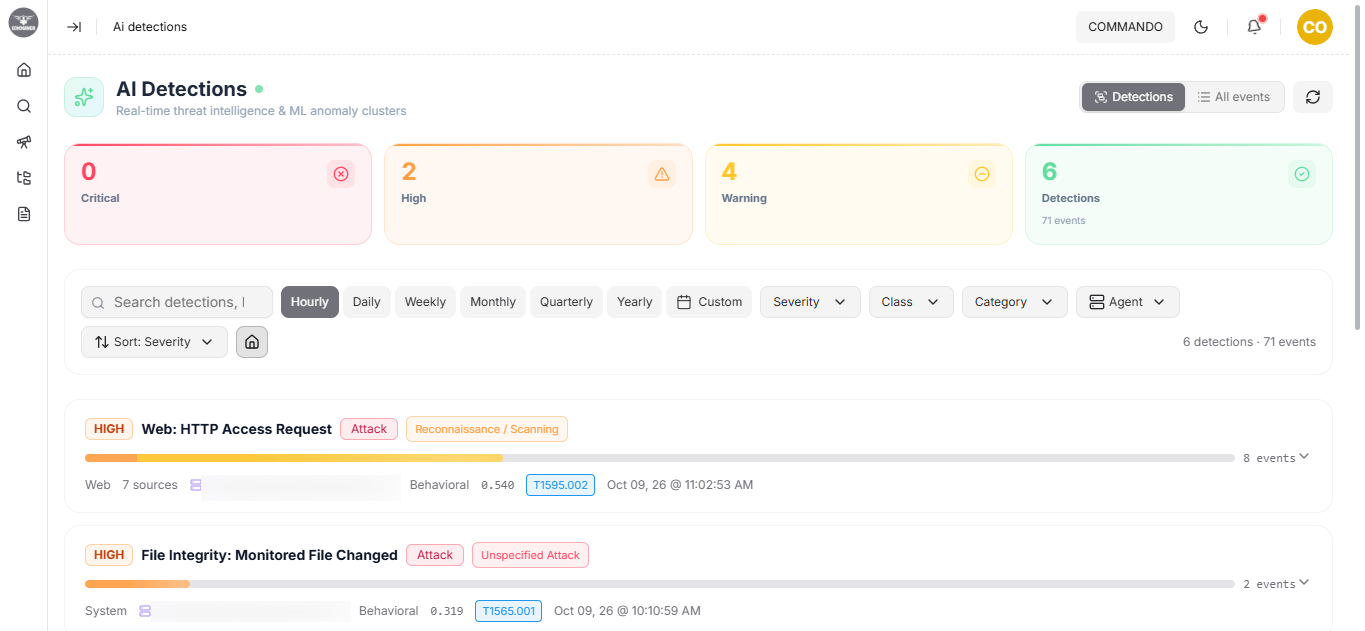
SoldierX AI SIEM's AI Engine continuously watches every event across your environment, building a clear picture of what's normal for your organization specifically, not a generic industry average, so it can immediately recognize what isn't.
Confidence Through Agreement
When multiple independent signals point to the same activity, SoldierX AI SIEM surfaces it as an Ensemble detection, the clearest, highest-confidence read the platform can give you.
Two independent signals agreeing is worth more than either one alone.
Six-Class Triage
Every detection lands in one of six classes, so severity always reflects what actually happened:
Attack and Ambiguous activity always receive full priority, so nothing potentially hostile gets quietly buried.
Analyst Feedback Loop
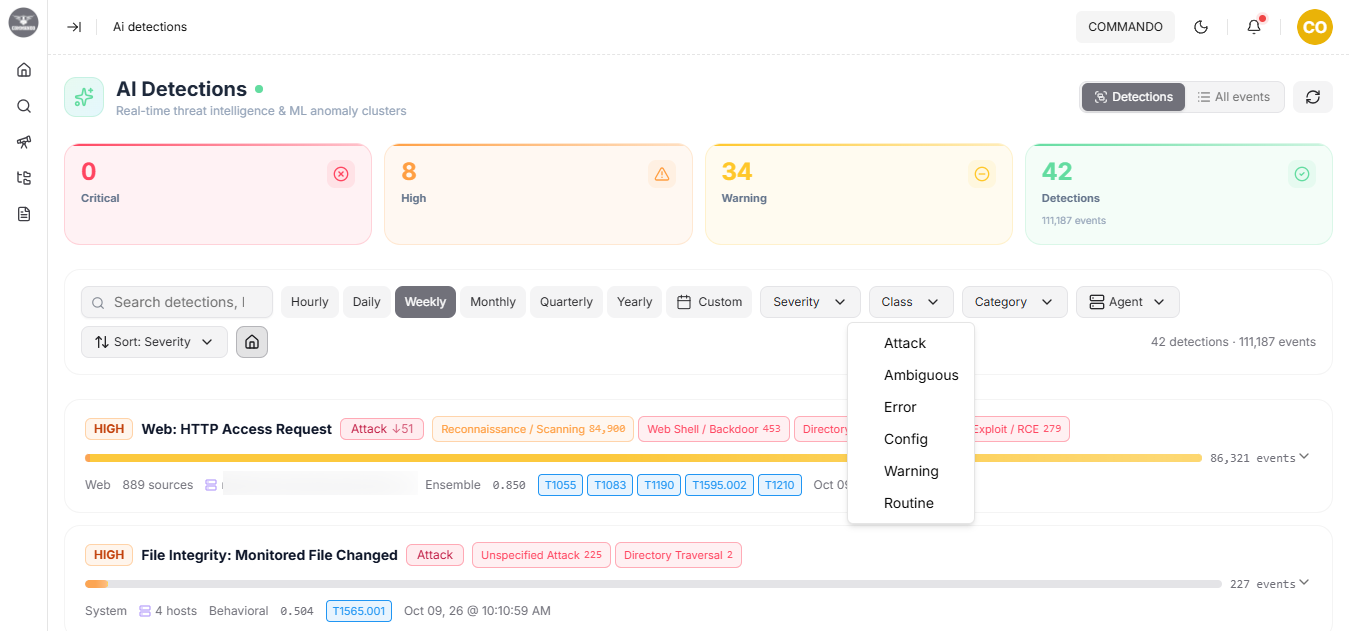
Your analysts mark detections as False Positive, True Positive, or clear a prior verdict, refining how future activity is classified.
Every verdict is preserved for a complete audit record. Nothing is ever deleted or hidden.
Recognized Patterns
Attack Types Recognized
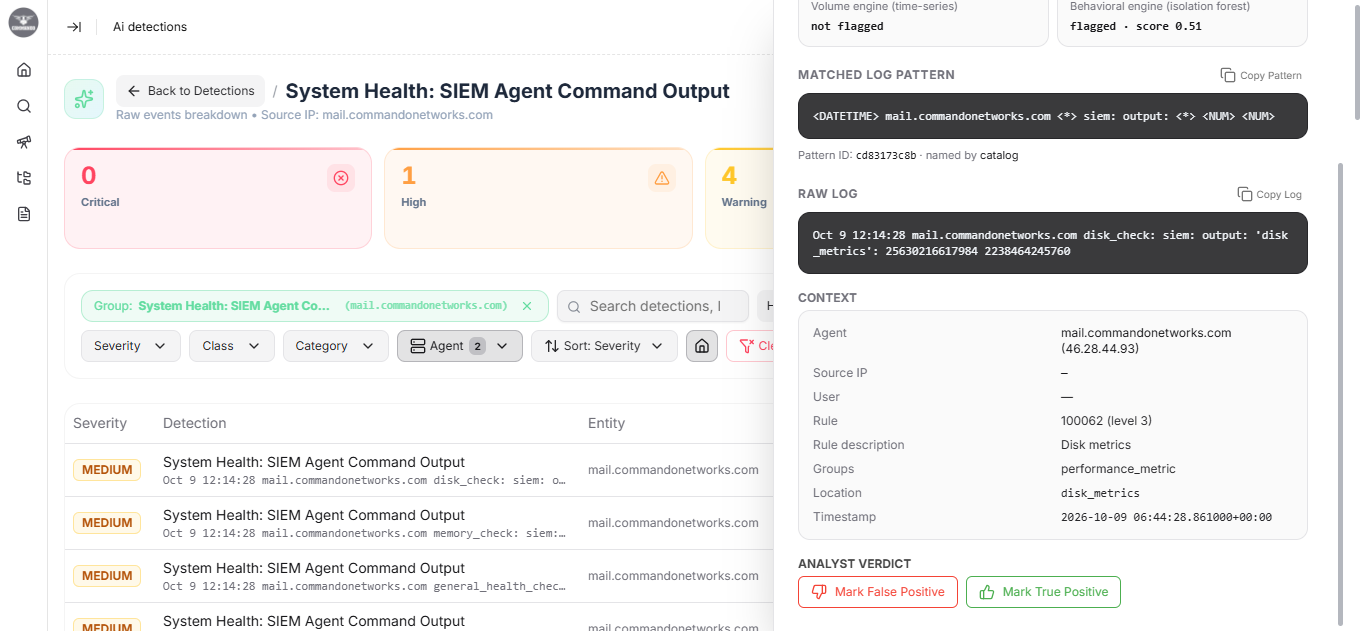
Detections are further classified by the specific kind of hostile activity they resemble, giving your team immediate context without a manual lookup.
Credential Attacks
Brute force, password spraying, and credential stuffing patterns, caught even when spread thin across time.
Web & Injection Exploits
SQL injection, cross-site scripting, and remote code execution attempts against your web-facing assets.
Data Exfiltration
Unusual outbound volume and destinations, flagged whether it's a sudden spike or a slow, deliberate trickle.
Lateral Movement
Activity spreading between assets in a way that doesn't match your environment's normal traffic patterns.
Command & Control
Malware and backdoor communication patterns, flagged by the same continuous analysis that covers every event.
Use Cases
Uncover threats your environment has never seen before.
Zero-Day & Novel Attack Detection
Catch attack patterns that have never been seen before. The AI Engine doesn't need to have encountered the exact pattern already to flag something wrong.
Insider Threat Detection
Surface activity that deviates from a user or asset's own established behavior, even when every individual action looks authorized on its own.
Noise Reduction for Your SOC
The six-class triage system keeps routine and low-severity activity out of your high-priority queue, so your team's attention goes where it matters.
Continuous Improvement
Every False Positive and True Positive verdict your analysts submit feeds back into how future activity is classified.
Why Choose
SoldierX AI SIEM
for Anomaly Detection?
Two independent engines, a confidence signal you can trust, and a triage system built so nothing genuinely dangerous slips through.
Two Engines, One Verdict
Two independent engines run in parallel on every event, catching more than either one would alone.
Confidence You Can Trust
Ensemble scoring tells you immediately when two independent signals agree.
Nothing Gets Buried
A six-class system means Attack and Ambiguous activity always gets full attention.
Learns Your Environment
Baselines are built from your own historical activity, not a generic industry average.
Full Audit Trail
Analyst verdicts refine future detection but never delete the underlying record.